Czech Republic security reports
14,988 public Guard scan reports. Each shows the site’s score, risk level and indicative NIS2 / GDPR posture from public signals.
Across the directory
All scanned sites, all time
- Websites scanned
- 150,213001234567890012345678900123456789,001234567890012345678900123456789
- Average score
- 600012345678900123456789/of100001234567890012345678900123456789
- High or critical risk
- 25%0012345678900123456789%
- Countries
- 112001234567890012345678900123456789
801–850 of 14,988
- SStředisko volného času - DOMEČEK HOŘOVICE
domecekhorovice.cz
Government · Czech Republic
62Medium
NIS2 2 · GDPR 10
NIS2 2 · GDPR 10
The website domecekhorovice.cz represents a municipal leisure center named Středisko volného času - DOMEČEK HOŘOVICE, established in 2005 and serving the local community of Hořovice, Czech Republic. It offers cultural and educational activities primarily targeting children, youth, and families. The site provides event announcements, contact information, and terms of service documentation, reflecting a public sector non-profit business model with municipal backing. Technically, the website employs common web technologies including jQuery, Google Analytics, Google Tag Manager, Google Maps API, and Lightbox2 for image galleries. The site appears to be custom-built or uses an unknown CMS, with moderate performance and good mobile optimization. SEO and accessibility features are basic but functional. From a security perspective, the site uses HTTPS and includes no visible sensitive data exposure. However, it lacks security headers and does not provide privacy or cookie policies, which are compliance gaps. The use of third-party analytics implies moderate user tracking without explicit consent mechanisms. No incident response or vulnerability disclosure information is present. Overall, the website is legitimate, consistent with its municipal purpose, and safe for general audiences. Strategic improvements include implementing privacy and cookie policies, enhancing security headers, and improving accessibility and compliance to strengthen trust and security posture.
 Proplavani.cz
proplavani.cz
Retail · Czech Republic
75Medium
NIS2 — · GDPR —
NIS2 — · GDPR —
Proplavani.cz is a Czech Republic-based e-commerce retailer specializing in swimming accessories and sports swimwear, endorsed by Czech Olympian Martina Moravčíková. The business operates primarily online via a Shopify platform with two physical stores in Prague. The website is professionally designed, mobile-optimized, and provides comprehensive privacy and cookie policies compliant with GDPR. The technical infrastructure leverages Shopify's hosting and CDN services, integrating marketing and analytics tools such as Facebook Pixel and AVADA Cookies Bar. Security posture is strong with HTTPS enforced, though some security headers are missing and no explicit security policies or incident response contacts are publicly available. The domain WHOIS data is not publicly accessible, indicating privacy protection, which slightly reduces transparency but is common for e-commerce sites. Overall, the site is trustworthy, well-maintained, and targets general audiences interested in swimming products.
 RE/MAX Alfa
realitnikariera.cz
Real Estate · Czech Republic
74Medium
NIS2 17 · GDPR 85
NIS2 17 · GDPR 85
The website www.realitnikariera.cz serves as a professional career portal for RE/MAX Alfa, a leading real estate brokerage office in the Czech Republic. It offers comprehensive information about becoming a real estate agent, company mission, vision, strategy, and testimonials from current agents. The site is well-structured, content-rich, and targets individuals interested in real estate careers within the Czech market. Technically, it is built on WordPress with modern SEO and analytics tools, ensuring good performance and user experience. Security posture is solid with HTTPS and cookie consent mechanisms, though explicit security headers are not confirmed. WHOIS data is unavailable due to privacy protection, which is common and justified for business domains. Overall, the site is trustworthy, professional, and compliant with GDPR regulations.
- TTOP REALITY SERVIS, s.r.o.
remaxalfa.cz
Real Estate · Czech Republic
60Medium
NIS2 2 · GDPR 85
NIS2 2 · GDPR 85
RE/MAX Alfa is a professional real estate agency operating primarily in the Czech Republic, offering a wide range of services including property sales, rentals, appraisals, auctions, and legal support. The company is part of the international RE/MAX network and positions itself as a market leader with a strong focus on customer satisfaction and high-quality service delivery. The website is well designed, multilingual, and provides comprehensive information about services, agents, and legal policies. Technically, the site is built on WordPress with modern plugins and SEO optimizations, ensuring good performance and user experience. Security measures include HTTPS and Google reCAPTCHA, although additional security headers could enhance protection. The absence of WHOIS data is a notable gap, but the overall digital presence and business information suggest a legitimate and trustworthy operation.
 Gymnathlon Foundation
kidslovesport.org
Non-profit · Czech Republic
75Medium
NIS2 — · GDPR —
NIS2 — · GDPR —
Gymnathlon Foundation is a Czech non-profit organization dedicated to providing sports scholarships and organizing sports activities for disadvantaged children, particularly those from single-parent and low-income families. The website is professionally designed using the Framer platform and incorporates modern analytics and cookie consent mechanisms, indicating a moderate level of digital maturity. However, the absence of explicit privacy and terms of service policies, as well as the lack of contact information, limits transparency and user trust. The security posture is adequate with HTTPS enabled but lacks advanced security headers and vulnerability disclosure policies. The WHOIS data shows an unusual future domain creation date, which may be a data error but slightly reduces trustworthiness. Overall, the website is functional and serves its non-profit mission but would benefit from enhanced compliance and security documentation.
 TJ Spartak Hořovice, z.s.
plavanihorovice.cz
Other · Czech Republic
46High
NIS2 17 · GDPR 60
NIS2 17 · GDPR 60
TJ Spartak Hořovice is a local Czech sports club specializing in swimming and modern pentathlon. The website serves as an information hub for club members and the local community, providing event calendars, news updates, photo galleries, and training schedules. The club operates as a non-profit entity, focusing on youth and amateur sports activities in the Hořovice region. The site is well maintained with consistent branding and relevant content for its target audience. Technically, the website is built on Joomla CMS with supporting frameworks such as Bootstrap and UIkit, leveraging jQuery and Google Fonts for enhanced user experience. The site is mobile optimized and includes a cookie consent mechanism, reflecting a moderate level of digital maturity. Performance is moderate with room for improvement in accessibility and SEO. From a security perspective, the site uses HTTPS but lacks several important security headers like Content-Security-Policy and HSTS, which could enhance protection against common web threats. No critical vulnerabilities or exposed sensitive data were detected. Privacy compliance is basic, with a cookie consent banner present but no explicit privacy policy or terms of service pages found. Overall, the website presents a moderate risk profile with good business credibility but could benefit from improved security practices and enhanced privacy documentation. Strategic recommendations include implementing security headers, publishing a comprehensive privacy policy, and maintaining up-to-date software to mitigate potential risks.
 Masáže Hořovice Martin Crk
masaze-martincrk.cz
Hospitality · Czech Republic
37High
NIS2 2 · GDPR 10
NIS2 2 · GDPR 10
Masáže Hořovice Martin Crk is a small local business providing massage and wellness services in the Czech Republic. The website presents a professional and clean design with clear contact information and a focus on natural massage oils and stress relief. The business is relatively new, founded in 2022, and targets general consumers seeking relaxation and physical well-being. The site uses WordPress CMS with common plugins such as Yoast SEO and jQuery, indicating a standard modern web infrastructure. Performance and mobile optimization are adequate, though accessibility features are basic. Security posture is good with HTTPS enabled and no visible vulnerabilities, but lacks advanced security headers and formal security policies. Privacy compliance is weak due to absence of privacy and cookie policies. Overall, the website is trustworthy for its business purpose but would benefit from enhanced privacy and security practices.
Retail · Czech Republic
64Medium
NIS2 — · GDPR —
NIS2 — · GDPR —
2Racing.cz is a Czech Republic-based e-commerce website specializing in the sale of automotive parts focused on racing, rally, and tuning enthusiasts. The site offers a wide range of products including racing seats, suspension components, filters, and accessories from reputable brands such as Strongflex, Koni, Sparco, and others. The business targets motorsport hobbyists and professionals seeking specialized car parts. The website is professionally designed with clear navigation and product categorization by car brand and year, supporting a good user experience.
 HMS Stavby
hms-stavby.cz
Real Estate · Czech Republic
40High
NIS2 2 · GDPR 10
NIS2 2 · GDPR 10
HMS Stavby is a small construction company based in the Czech Republic, operating since 2012. The website presents basic information about the business and its services, targeting a general audience interested in building and construction. The site is built on WordPress using the Divi theme, with standard web technologies such as jQuery and Google Fonts. The hosting provider is WEDOS, consistent with the Czech location. The website has basic mobile optimization and moderate performance but lacks advanced SEO and accessibility features. Security posture is moderate with HTTPS enabled but no security headers detected and an expired domain status which poses a risk. Privacy compliance is minimal with no privacy policy or terms of service found, though a cookie consent mechanism is implemented. Overall, the site is functional but lacks comprehensive security and compliance measures.
 AutoTužil
autotuzil.cz
Transportation · Czech Republic
60Medium
NIS2 2 · GDPR 25
NIS2 2 · GDPR 25
AutoTužil is a small automotive service provider based in the Czech Republic offering a wide range of vehicle repair and maintenance services including nonstop auto repair, air conditioning servicing, diagnostics, and sale of auto accessories. The website is professionally designed with clear navigation and good mobile optimization, targeting vehicle owners in the local region. The business appears well-established with a founding year of 2004 indicated in the footer, although domain registration details are unavailable, which introduces some uncertainty about domain legitimacy. Technically, the site uses modern frontend libraries such as Bootstrap and jQuery, and integrates Google Analytics and Tag Manager for user tracking. Security posture is moderate with HTTPS enabled but lacking security headers and a privacy policy, which are recommended for compliance and trust. Overall, the website is functional and trustworthy for its business purpose but would benefit from improved transparency and security practices.
 Látky Wiedrman levná podšívka tyl a šusťák
latky-wiedrman.cz
Retail · Czech Republic
54Medium
NIS2 2 · GDPR 10
NIS2 2 · GDPR 10
The website www.latky-wiedrman.cz appears to be a retail business specializing in selling fabrics and related materials such as linings, tulle, organza, and elastic satin primarily targeting customers in the Czech Republic. However, the site content is fully restricted behind a password form, limiting public access and visibility into the full scope of their offerings and business details. The lack of publicly accessible content and absence of WHOIS registration data reduces transparency and trustworthiness. Technically, the site uses Matomo analytics and Google Fonts but lacks visible security headers and privacy compliance mechanisms. The overall security posture is minimal with no clear evidence of GDPR compliance or incident response readiness. The restricted access may be justified for business confidentiality but significantly impacts the ability to assess the website's quality and security comprehensively.
 JAN VLČEK
vlcek-stavby.cz
Real Estate · Czech Republic
40High
NIS2 2 · GDPR 10
NIS2 2 · GDPR 10
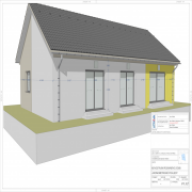
Jan Vlček operates as an authorized builder and member of the Chamber of Authorized Engineers and Technicians in Construction, providing construction management and project services primarily in the Czech Republic. The business targets individuals and companies seeking professional construction oversight and authorized building services, with a focus on civil, residential, and industrial projects. The website reflects a small, local service provider with over 30 years of industry experience, supported by professional certifications and clear contact information. Technically, the website is built on WordPress using common plugins such as Contact Form 7 and Revolution Slider. It employs jQuery 1.7.2 and Google Maps API for functionality. The site shows moderate performance and basic mobile optimization but uses outdated JavaScript libraries and lacks advanced SEO and accessibility features. No analytics or tracking services are detected, indicating minimal user tracking. From a security perspective, the site uses HTTPS but lacks important security headers like Content-Security-Policy and Strict-Transport-Security. The use of outdated libraries presents potential vulnerabilities. No privacy or cookie policies are present, indicating compliance gaps with GDPR and related regulations. Contact information is clearly provided, but no incident response or security policies are visible. Overall, the website is functional and moderately professional but requires improvements in security, privacy compliance, and technical modernization to enhance trustworthiness and protect user data effectively.
- TTAC-TAC agency s.r.o.
tac-tac.cz
Retail · Czech Republic
48High
NIS2 2 · GDPR 10
NIS2 2 · GDPR 10
TAC-TAC agency s.r.o. is a small Czech advertising company specializing in promotional products and client advertising services. The website presents basic information about the company and its offerings, targeting businesses seeking advertising solutions. The company has been established since 2000, indicating a stable presence in the local market. The website uses SuitableCMS and is hosted by Wedos, with integrations of common marketing and analytics tools such as Google Analytics, Google Tag Manager, Hotjar, and Google reCAPTCHA for bot protection. From a technical perspective, the website employs older technologies such as jQuery 1.7.2, which is outdated and poses security risks. The site lacks modern security headers and visible privacy or cookie policies, indicating compliance gaps with GDPR and other privacy regulations. The website is accessible without WAF or blocking mechanisms, but the security posture is moderate due to missing best practices and outdated libraries. Security-wise, the site uses HTTPS (implied by origin-trial meta tag referencing HTTPS Google services) and reCAPTCHA, but lacks explicit security headers and incident response information. No vulnerabilities such as exposed credentials or SQL injection are visible, but the outdated jQuery version is a concern. Contact information is minimal but present, with a company email and phone number displayed. Overall, the website scores moderately on AI evaluation with strengths in business credibility and basic technical implementation but weaknesses in privacy compliance and security best practices. Strategic improvements in updating technology, adding privacy and cookie policies, and enhancing security headers would significantly improve the site's security posture and compliance.
- ČČESKOMORAVSKÝ POHÁR RALLYE
cmpr.cz
Transportation · Czech Republic
42High
NIS2 2 · GDPR 10
NIS2 2 · GDPR 10
ČESKOMORAVSKÝ POHÁR RALLYE (ČMPR) operates as an organizer and promoter of rally competitions primarily targeting motorsport enthusiasts in the Czech Republic. The website serves as the official platform for event calendars, results, rules, and news related to the rally cup. The business is positioned as a niche regional motorsport event organizer with a small organizational size and a history dating back to 2010. The site content is primarily in Czech and focuses on rally event information and community engagement via social media channels such as Facebook and YouTube. Technically, the website is built on WordPress using the Blocksy theme and leverages common web technologies including jQuery, Yoast SEO for search optimization, Google reCAPTCHA v3 for form security, and Swiper.js for UI components. Hosting appears to be provided by a Czech hosting provider (cesky-hosting.eu). The site demonstrates moderate performance and good mobile optimization, with basic accessibility features and good SEO practices. From a security perspective, the site enforces HTTPS and integrates Google reCAPTCHA to protect forms from abuse. However, it lacks visible security headers and does not publish security policies or incident response contacts. Privacy and cookie policies are absent, indicating gaps in compliance with GDPR and related regulations. No vulnerabilities or exposed sensitive data were detected in the analysis. Overall, the website presents a professional and trustworthy front for its business purpose but would benefit from enhanced privacy compliance, security policy transparency, and improved contact information availability to strengthen user trust and regulatory adherence.
 CENDIS, s.p.
cendis.cz
Government · Czech Republic
67Medium
NIS2 17 · GDPR 10
NIS2 17 · GDPR 10
CENDIS, s.p. is a Czech government-related entity specializing in transportation information systems under the Ministry of Transport of the Czech Republic. The organization provides key ICT solutions and services such as electronic highway vignettes, unified railway tickets, electronic toll supervision, and various training and certification programs. Their target audience includes drivers, transport operators, public transport passengers, and government officials. The website reflects a professional and consistent brand image with a focus on transparency and public service. Technically, the site is built on WordPress using Elementor and Smart Slider 3, with Google Analytics integrated for visitor tracking. The site is mobile-optimized and offers good navigation and content relevance. Security posture is adequate with HTTPS and cookie consent mechanisms, but lacks some advanced security headers and explicit incident response contacts. WHOIS data is missing, which reduces domain trustworthiness, but the official nature of the site and linked government registries support legitimacy. Overall, the site is a reliable source of transportation ICT information and services in the Czech Republic.
 NIVEA
nivea.cz
Retail · Czech Republic
65Medium
NIS2 17 · GDPR 25
NIS2 17 · GDPR 25
NIVEA.cz is the Czech Republic localized website for the globally recognized skincare brand NIVEA, owned by Beiersdorf AG. The site offers a comprehensive catalog of skincare and cosmetic products, along with tips and advice for skin and body care. The website targets general consumers interested in personal care products and maintains a strong brand presence consistent with NIVEA's global identity. Technically, the site is built on the Sitecore CMS platform, employs modern web technologies, and integrates multiple analytics and marketing tools such as Google Analytics, Google Tag Manager, and Consent Manager for GDPR compliance. The site is mobile-optimized and provides a professional user experience with clear navigation and rich content. Security-wise, the website enforces HTTPS, uses standard security headers, and implements cookie consent mechanisms, reflecting a mature security posture. However, it lacks publicly available explicit security policies and incident response contacts, which could be improved. The domain WHOIS data is unavailable, likely due to registry policies, which slightly reduces transparency but does not detract significantly from the site's legitimacy given the brand's reputation. Overall, the website is well-maintained, secure, and compliant with privacy regulations, serving as a reliable digital presence for NIVEA in the Czech market.
 Nadační fond Flaminia
nfflaminia.cz
Non-profit · Czech Republic
59Medium
NIS2 10 · GDPR 10
NIS2 10 · GDPR 10
Nadační fond Flaminia is a Czech non-profit foundation established in 2007, dedicated to supporting mental health and psychological wellbeing projects for children and youth. The organization collaborates with various partner projects and runs awareness campaigns to promote mental health care as equally important as physical health. Their website reflects a professional and consistent brand image, providing clear contact information and detailed descriptions of their initiatives and supported projects. Technically, the website uses modern web technologies including Bootstrap, jQuery, FontAwesome, and Google Fonts, with good mobile optimization and SEO practices. The site is accessible and well-structured, though it uses multiple versions of Bootstrap and jQuery which could be streamlined. No CMS or hosting provider details were detected. From a security perspective, the site enforces HTTPS and avoids exposing sensitive data, but lacks important security headers and privacy/cookie policies, which are compliance gaps. No WHOIS data was found for the domain, which reduces trustworthiness and raises questions about domain registration legitimacy. No analytics or tracking scripts were detected, indicating minimal user tracking. Overall, the site is trustworthy and professional in content and presentation but would benefit from improved privacy compliance and security hardening. The lack of WHOIS data is a notable concern that should be investigated further.
 Qminers
qminers.com
Finance · Czech Republic
51Medium
NIS2 17 · GDPR 50
NIS2 17 · GDPR 50
Qminers is a specialized software development company focused on algorithmic trading, providing a Central European hub for top-tier professionals in quantitative finance and technology. The company emphasizes improving global markets through advanced software solutions and a meritocratic, knowledge-sharing culture. Their website reflects a professional and consistent brand image, targeting expert audiences in finance and technology sectors. Technically, the site uses modern web technologies with embedded video content and is hosted by a reputable provider. Security posture is adequate with HTTPS enabled but lacks advanced security headers and published policies. Privacy compliance is limited, with no privacy or terms of service pages found, though a cookie consent banner is present. Overall, the site is safe, professional, and trustworthy but could improve in compliance and security transparency.
 Crestyl
crestyl.com
Real Estate · Czech Republic
53Medium
NIS2 2 · GDPR 50
NIS2 2 · GDPR 50
Crestyl is a well-established real estate development company based in the Czech Republic, specializing in multi-sector projects including residential, office, and retail properties. The company positions itself as a market leader with a strong portfolio and multiple industry awards, reflecting its prominence and credibility in the real estate sector. The website content is professionally presented, targeting investors, tenants, and clients interested in high-quality real estate developments. Technically, the website employs modern JavaScript libraries such as jQuery and Leaflet, integrates Google Analytics and Tag Manager for tracking, and implements a granular cookie consent mechanism, indicating a moderate level of digital maturity. Security-wise, the site uses HTTPS and cookie consent but lacks visible security headers and published security policies, suggesting room for improvement in security posture and compliance documentation. Overall, the website is accessible, well-branded, and trustworthy, though it would benefit from enhanced privacy and security disclosures to align with best practices.
- Cesta z krize, z.ú.
linkapsychickepomoci.cz
Non-profit · Czech Republic
50Medium
NIS2 2 · GDPR 88
NIS2 2 · GDPR 88
The website linkapsychickepomoci.cz represents a non-profit organization named Cesta z krize, z.ú., providing free, anonymous, and 24/7 psychological crisis support services primarily to adults in the Czech Republic. The service offers telephone and chat support to individuals facing acute psychological distress or crisis situations. The organization is government co-financed and partners with other NGOs, positioning itself as a trusted social service provider in the mental health support sector. Technically, the website employs modern web technologies including Google Tag Manager, Cookiebot for cookie consent management, and Smartsupp for live chat functionality. The site is hosted by Active24 and demonstrates moderate performance with good mobile optimization and basic accessibility features. SEO and metadata are present but could be enhanced for better discoverability. From a security perspective, the site uses HTTPS and implements cookie consent mechanisms, but lacks visible security headers and explicit security policies. No vulnerabilities or exposed sensitive data were detected in the HTML content. The absence of a privacy policy and terms of service pages, as well as no security.txt file, indicates areas for compliance and security improvement. Overall, the website is safe, professional, and trustworthy, with a clear focus on mental health crisis support. Strategic recommendations include enhancing security headers, publishing comprehensive privacy and terms policies, and improving accessibility compliance to strengthen user trust and regulatory adherence.
- Cesta z krize, z.ú.
linkaztracenedite.cz
Non-profit · Czech Republic
53Medium
NIS2 2 · GDPR 88
NIS2 2 · GDPR 88
The website 'Linka pro rodinu a školu' is a Czech non-profit social service platform operated by 'Cesta z krize, z.ú.' focused on supporting families, children, and adults in crisis situations, particularly related to missing children and school or family problems. It offers telephone crisis intervention, online chat support, and professional counseling, positioning itself as a trusted and officially recognized service with backing from national and European institutions. The site targets a broad audience including families, educators, and the general public. Technically, the website employs modern web technologies such as Google Tag Manager and Cookiebot for consent management, with a moderate performance profile and good mobile optimization. Hosting is provided by Active24, consistent with the domain registration data. The site implements a comprehensive cookie consent mechanism with granular user controls, reflecting a good level of privacy compliance, although explicit privacy policy and terms of service pages are not clearly found in the provided content. From a security perspective, the site uses HTTPS (implied by external scripts loaded via HTTPS), but no explicit security headers or advanced security policies are evident in the HTML content. No vulnerabilities or exposed sensitive data were detected. The WHOIS data is transparent and consistent with the organization's profile, indicating a legitimate and stable domain registration. Overall, the website demonstrates a solid risk posture with good privacy compliance and business credibility. Recommendations include enhancing security headers, publishing explicit security and incident response policies, and improving accessibility features to further strengthen the site's security and compliance posture.
 Virtuplex
virtuplex.space
Technology · Czech Republic
69Medium
NIS2 17 · GDPR 80
NIS2 17 · GDPR 80
Virtuplex operates the world's largest commercial virtual reality labs with locations in Dubai, Bratislava, and Prague. The company specializes in providing VR solutions that allow clients to experience and interact with buildings, products, and spaces before they are physically built. Their market position is strong, supported by over 100 projects and a diverse client base across industries such as real estate, urban planning, retail, manufacturing, and defense. The website reflects a mature digital presence with modern technologies and comprehensive service descriptions.
- LLaddobar studio
laddobar.cz
Technology · Czech Republic
43High
NIS2 2 · GDPR 25
NIS2 2 · GDPR 25
Laddobar.cz is a small personal or studio website operated by Ladislav Pelcl, focusing on web hosting and web development services. The site is currently in a development phase with minimal content and references to an older website and a related hosting business. The domain is well-established, created in 2002, indicating a long-term presence in the web hosting space. Technically, the site uses basic HTML and CSS without modern frameworks or CMS, and lacks mobile optimization and accessibility features. Security posture is weak due to absence of HTTPS, security headers, and privacy policies. No analytics or advertising tools are detected, and the site content is safe for general audiences. Overall, the site demonstrates moderate trustworthiness but requires significant improvements in security and privacy compliance to enhance credibility and user trust.
- AAuto Sport Klub Hořovice
askhorovice.cz
Transportation · Czech Republic
42High
NIS2 17 · GDPR 25
NIS2 17 · GDPR 25
Auto Sport Klub Hořovice operates as a local motorsport club primarily focused on organizing rally events such as Rallye Hořovice. The website serves as an information hub for participants, media, and fans, providing event schedules, official documents, and partner links. The business is small-sized, rooted in the Czech Republic, and has been established since 2003, as supported by domain registration data. The target audience includes motorsport enthusiasts and regional participants. Technically, the website is built on WordPress with common JavaScript libraries like jQuery and MooTools, offering basic mobile optimization and moderate performance. Security posture is adequate with HTTPS enabled and GDPR cookie consent implemented, but lacks advanced security headers and explicit privacy policies. No contact emails or phone numbers are directly provided, which limits direct communication channels. Overall, the website is functional and trustworthy for its niche but could benefit from enhanced privacy and security disclosures.
- GGe-Baek Hosin Sool
tkd.cz
Other · Czech Republic
60Medium
NIS2 17 · GDPR 25
NIS2 17 · GDPR 25
Ge-Baek Hosin Sool is a well-established traditional Taekwon-Do ITF school based in the Czech Republic, focusing on martial arts training with an emphasis on moral and traditional values rather than competitive sports. The website serves as an information hub for recruitment, member resources, event schedules, and media galleries, targeting individuals and families interested in Taekwon-Do. The school maintains partnerships with other martial arts organizations and receives sponsorship from various municipalities, indicating a strong community presence. Technically, the website uses modern web technologies including Bootstrap and Google Analytics, with responsive design and multilingual support. HTTPS is enforced, and Google Analytics consent is configured to deny ad and analytics storage by default, reflecting a basic level of privacy awareness. However, the site lacks explicit privacy and security policies, terms of service, and direct contact information, which are areas for improvement. From a security perspective, the site shows good SSL configuration but lacks security headers and formal incident response or vulnerability disclosure mechanisms. No WHOIS data is available due to privacy protection, but the website's professional appearance and affiliations suggest legitimacy. Overall, the site scores well on content quality and business credibility but could enhance privacy compliance and security posture. Strategic recommendations include implementing comprehensive privacy and security policies, adding terms of service, improving contact transparency, and deploying security headers to strengthen trust and compliance.
- TTenisová škola Zýka Hořovice
tenisovaskola-zyka.cz
Other · Czech Republic
50Medium
NIS2 2 · GDPR 25
NIS2 2 · GDPR 25
Tenisová škola Zýka Hořovice is a small, family-run tennis school based in the Czech Republic with over 20 years of experience. The business focuses on tennis training for children and competitive players, offering services such as racket stringing and court rentals. The website is built on the eStránky.cz platform and integrates basic technologies like jQuery and Facebook SDK for social media connectivity. However, the site lacks critical compliance documents such as privacy and cookie policies and does not provide contact emails, limiting its professional and compliance posture. The absence of WHOIS data raises concerns about domain legitimacy, although the site content appears genuine and targeted at local tennis enthusiasts.
- ZS Hořovice
zs-horovice.cz
Other · Czech Republic
60Medium
NIS2 2 · GDPR 25
NIS2 2 · GDPR 25
The website www.zs-horovice.cz represents a local sports facility, specifically the ice stadium in Hořovice, Czech Republic. The site provides basic information about the stadium's location and purpose but lacks detailed business or contact information. It is built on the Wix platform, indicating a moderate level of digital maturity with standard web technologies and hosting. The technical infrastructure is typical for Wix sites, with no advanced frameworks or custom backend detected. Security posture is adequate with HTTPS enabled and no visible vulnerabilities, but the absence of explicit security headers and privacy policies limits compliance and trust. The lack of WHOIS data due to privacy protection or unregistered domain status reduces the domain's trustworthiness. Overall, the site serves informational purposes for a small local entity but requires improvements in transparency, privacy compliance, and security best practices to enhance credibility and user trust.
Hospitality · Czech Republic
45High
NIS2 2 · GDPR 25
NIS2 2 · GDPR 25
Bazén Hořovice is a municipal swimming pool and aquapark facility operated by the Městské sportovní centrum Hořovice, a city sports organization in the Czech Republic. The website provides comprehensive information about the indoor swimming pool, summer aquapark, services such as refreshments, gym access, and specialized massages. It targets local residents and visitors seeking recreational aquatic activities. The business operates as a public service entity with a local government affiliation, emphasizing community engagement and leisure services. Technically, the website is built on WordPress CMS, utilizing plugins like Smart Slider 3 and integrating YouTube videos for enhanced user experience. The site is hosted by hosting-profi.cz and demonstrates moderate performance with good mobile optimization. SEO and accessibility are basic but functional. The cookie consent mechanism complies with GDPR requirements, although privacy and terms of service policies are missing. From a security perspective, the site enforces HTTPS and avoids exposing sensitive data. However, it lacks advanced security headers and published security policies or incident response contacts. No vulnerabilities or suspicious activities were detected. The WHOIS data confirms domain legitimacy with consistent registration details and appropriate domain age. Overall, the website is a trustworthy, well-maintained municipal service portal with room for improvement in privacy compliance and security hardening. Strategic recommendations include publishing privacy and terms policies, enhancing security headers, and improving accessibility features.
 Městské sportovní centrum Hořovice
horovicesport.cz
Government · Czech Republic
41High
NIS2 17 · GDPR 25
NIS2 17 · GDPR 25
Městské sportovní centrum Hořovice is a municipal sports center serving the local community of Hořovice, Czech Republic. It provides sports facilities including a sports hall, aquapark, and sauna, and supports local sports clubs by providing schedules and information. The organization operates under the City of Hořovice and targets local residents and sports enthusiasts. The website is built on WordPress with modern plugins and offers a good user experience with clear navigation and mobile optimization. GDPR compliance is implemented with cookie consent mechanisms and a privacy policy. Contact information is clearly provided, including a designated Data Protection Officer. Security posture is good with HTTPS and no visible vulnerabilities, though security headers could be improved. Overall, the website is trustworthy and professionally maintained, reflecting a legitimate public service entity.
- KKlub Labe Hořovice
klublabe.cz
Hospitality · Czech Republic
41High
NIS2 2 · GDPR 10
NIS2 2 · GDPR 10
Klub Labe Hořovice is a local entertainment venue based in the Czech Republic, specializing in live concerts, podcasts, and nightlife events. The website serves as a platform to showcase upcoming events, facilitate ticket sales through a reputable external provider, and offer venue rental services. The target audience primarily consists of local residents and visitors interested in cultural and music events in the Hořovice and Beroun regions. The business operates on a small scale with a focus on hospitality and entertainment services. Technically, the website is built using modern web technologies including Nuxt.js and Vue.js, indicating a contemporary and maintainable infrastructure. The site is mobile optimized and provides a good user experience with clear navigation and relevant content. However, some areas such as accessibility and SEO could be further enhanced. The hosting and domain registration are consistent with the business location, and the site uses HTTPS ensuring secure communication. From a security perspective, the website enforces HTTPS and avoids exposing sensitive data. However, it lacks several security headers and does not provide visible privacy or cookie policies, which are important for GDPR compliance. There is no public incident response or vulnerability disclosure information, which could be improved to enhance trust and security posture. The site does not appear to use analytics or tracking services, minimizing privacy concerns but also limiting marketing insights. Overall, Klub Labe Hořovice presents a professional and trustworthy online presence for a local entertainment venue. Strategic improvements in privacy compliance, security headers, and transparency around data protection would strengthen its security posture and regulatory adherence. The business is well positioned in its local market with a clear service offering and digital maturity appropriate for its size and sector.
- OObec Osov
osov.cz
Government · Czech Republic
55Medium
NIS2 17 · GDPR 10
NIS2 17 · GDPR 10
Obec Osov is the official municipal website for the village of Osov in the Czech Republic, providing residents and visitors with local government information, community services, event announcements, and historical context. The site serves as a central hub for municipal communication and public service access, targeting local citizens and stakeholders. The business model is that of a small government entity focused on transparency and community engagement. Technically, the website is built on a custom PHP-based CMS with legacy JavaScript libraries such as jQuery 1.11.0 and Lightbox.js. It integrates Google Analytics and Google Tag Manager for visitor tracking but lacks modern security headers and cookie consent mechanisms. Hosting appears to be with a Czech provider (WEDOS), and the site performance and mobile optimization are basic but functional. From a security perspective, the site shows moderate maturity with no visible critical vulnerabilities but suffers from outdated libraries, lack of security headers, and missing cookie consent, which may expose it to some risks and compliance issues under GDPR. The WHOIS data confirms the domain's legitimacy and long-standing presence, consistent with the municipal nature of the site. Overall, the website is trustworthy and serves its purpose well but would benefit from technical and security improvements to enhance compliance, user privacy, and protection against emerging threats.
Other · Czech Republic
44High
NIS2 17 · GDPR 25
NIS2 17 · GDPR 25
The website www.vhsb.cz represents the Vojenské Historické Sdružení Brdy, a small community organization dedicated to preserving and sharing the military history of the Brdy region in the Czech Republic. The site offers historical articles, photo galleries, and information about local events, targeting military history enthusiasts and the local community. The business model appears to be non-profit or community-driven with a niche focus. Technically, the website is built on IceCMS, a less common content management system, and uses standard HTML and CSS. The site is accessible with HTTPS enabled but lacks modern security headers and advanced technical features. Mobile optimization and accessibility are basic, and SEO practices are minimal. There are no analytics or tracking scripts detected, indicating a low level of user tracking. From a security perspective, the site has a basic security posture with HTTPS but lacks security headers and formal privacy or cookie policies, which are critical for GDPR compliance. No contact information or incident response details are provided, limiting transparency and user trust. The absence of WHOIS data for the domain raises concerns about domain registration legitimacy and reduces overall trustworthiness. Overall, the website is functional and provides relevant content for its audience but requires improvements in privacy compliance, security best practices, and transparency to enhance trust and meet modern standards.
Media · Czech Republic
47High
NIS2 17 · GDPR 33
NIS2 17 · GDPR 33
mistecko.cz is a Czech online magazine providing cultural, artistic, and lifestyle content targeted at creators, artists, and culture enthusiasts. The website offers news, tips, and tutorials related to various creative passions. The business operates in the media sector with a small scale and a niche market position. Technically, the site uses standard web technologies including Matomo for analytics and Google Adsense for advertising. The site is mobile optimized with good navigation and content relevance. Security posture is moderate with HTTPS enabled but lacks security headers and cookie consent mechanisms. WHOIS data shows inconsistencies with a future domain creation date, which raises questions about domain legitimacy. Overall, the website is functional and content-rich but requires improvements in privacy compliance and security practices.
 Praskoleská společnost sv. Prokopa
svprokop.cz
Non-profit · Czech Republic
40High
NIS2 2 · GDPR 10
NIS2 2 · GDPR 10
The website www.svprokop.cz represents the Praskoleská společnost sv. Prokopa, a small local cultural society in the Czech Republic focused on organizing cultural events and preserving local heritage sites such as chapels and churches. The site content is primarily in Czech and includes announcements for cultural events, indicating an active community engagement. Technically, the website is built on WordPress 4.9.28 with plugins such as Yoast SEO and Contact Form 7, and uses Bootstrap 3.3.7 for styling. While the site is served over HTTPS with valid SSL, it uses outdated software versions and lacks modern security headers, which could expose it to vulnerabilities. No privacy, cookie, or terms of service policies are present, and no contact emails or phone numbers are explicitly provided, limiting user trust and compliance with privacy regulations. WHOIS data is unavailable, which reduces domain trustworthiness and raises concerns about domain legitimacy. Overall, the site is functional but requires updates and improvements in security, privacy compliance, and transparency to enhance trust and protect users.
- SSTŘELA Žebrák, z.s.
strelazebrak.cz
Non-profit · Czech Republic
40High
NIS2 2 · GDPR 10
NIS2 2 · GDPR 10
STŘELA Žebrák, z.s. is a Czech non-profit association founded in 2019, dedicated to educational and leisure activities for children and youth, focusing on athletics, tourism, and summer camps. The organization maintains a strong local community presence with multiple social media channels and partnerships with regional entities. The website serves as an information hub for their activities, events, and registration forms, reflecting a clear mission to engage youth in meaningful activities. Technically, the website employs modern front-end technologies including Tailwind CSS and jQuery, hosted likely by WEDOS, a Czech hosting provider. The site is mobile-optimized with good navigation and content structure, though some accessibility features could be improved. SEO practices are adequately implemented with proper meta tags and descriptive content. From a security perspective, the site uses HTTPS but lacks visible security headers and explicit security policies. No forms on the main page reduce attack surface, but cookie consent mechanisms are missing, which is a GDPR compliance gap. WHOIS data is transparent and consistent with the organization's profile, supporting legitimacy. Overall, the website is trustworthy and professionally maintained, with room for improvement in security hardening and privacy compliance. The risk level is low given the non-commercial nature and limited data collection, but enhancing security policies and cookie management would strengthen compliance and user trust.
- VVojenský újezd Brdy - výlety, turistické trasy, cyklostezky
vojujezd-brdy.cz
Hospitality · Czech Republic
43High
NIS2 17 · GDPR 45
NIS2 17 · GDPR 45
The website www.vojujezd-brdy.cz serves as an informational portal focused on tourism, hiking, cycling, and local history related to the former military area Brdy in the Czech Republic. It targets tourists and outdoor enthusiasts seeking less crowded natural areas. The site provides detailed descriptions of trails, accommodation options, and local services, monetized primarily through Google Adsense advertising. Technically, the site uses standard web technologies including HTML5, CSS, JavaScript, Google Fonts, and integrates Google Analytics and a consent management platform to comply with privacy regulations. The website is accessible without WAF or security challenges, but lacks explicit privacy and terms of service pages, and does not provide direct contact information, which limits user trust and compliance transparency. Security posture is moderate with HTTPS enabled but missing security headers. WHOIS data is unavailable, which reduces domain trustworthiness. Overall, the site is functional and relevant for its niche audience but could improve in privacy transparency, security best practices, and contact availability.
 Informační centrum Brdy
icbrdy.cz
Hospitality · Czech Republic
45High
NIS2 17 · GDPR 10
NIS2 17 · GDPR 10
Informační centrum Brdy operates as a regional tourist information center located in the Czech Republic, providing comprehensive guidance on the Brdy region's natural, cultural, and historical attractions. The center is integrated within the PilsnerGolf Resort Hořehledy and offers services including event information, accommodation booking, internet access, and equipment rental. The website is professionally designed using WordPress and Oxygen Builder, featuring good mobile optimization and clear navigation. It maintains a moderate performance profile and includes certifications that enhance its credibility. From a technical perspective, the site employs modern web technologies and plugins such as Contact Form 7 and Tiny Slider, ensuring interactive and user-friendly experiences. Security posture is solid with HTTPS enforced and no visible vulnerabilities, though the absence of security headers and cookie consent mechanisms suggests room for improvement in compliance and defense-in-depth strategies. The lack of WHOIS data reduces domain trust slightly but does not detract significantly from the overall legitimacy. Overall, the website presents a trustworthy and professional front for the information center, with clear contact details and partner affiliations. Strategic recommendations include implementing cookie consent for GDPR compliance, adding security headers, and publishing a formal security policy to enhance transparency and user trust.
- BBrdy - Hlavní stránka
brdy.org
Other · Czech Republic
44High
NIS2 2 · GDPR 35
NIS2 2 · GDPR 35
The website www.brdy.org serves as an informational portal dedicated to the Brdy region in the Czech Republic, focusing on its natural environment, historical background, military significance, and tourism. It targets enthusiasts, tourists, and locals interested in the region's heritage and nature. The site is built on Joomla CMS with modern web technologies such as Bootstrap, jQuery, and WebAuthn for enhanced login security. The content is well-structured, visually appealing, and mobile-optimized, providing a good user experience. However, the absence of explicit privacy and cookie policies indicates a gap in compliance with data protection regulations. Security-wise, the site uses HTTPS and some best practices like CSRF tokens and WebAuthn but lacks visible security headers. The WHOIS data is unavailable due to a malformed query response, which limits the ability to fully verify domain legitimacy and trustworthiness. Overall, the site is functional, content-rich, and safe but would benefit from improved transparency and compliance documentation.
- NNázev firmy s.r.o.
up4.cz
Technology · Czech Republic
50Medium
NIS2 17 · GDPR 25
NIS2 17 · GDPR 25
up4.cz is a Czech Republic-based small technology company specializing in the development of sophisticated custom software applications. Their offerings include web applications, Android and iOS apps, automation tools, GIS mapping systems, and data conversion bridges. The company emphasizes user-friendly, efficient software solutions tailored for demanding clients, with a business history dating back to 2001. The website presents a professional image with detailed service descriptions, client testimonials, and multiple contact channels, including a contact form with captcha and phone support. Social media presence on Twitter, Instagram, and Facebook supports their outreach. Technically, the website uses modern frontend technologies such as Bootstrap 5.2, jQuery, FontAwesome, and the Nette PHP framework. It is mobile optimized and includes cookie consent mechanisms compliant with GDPR principles. Google Analytics and Google Tag Manager are used for analytics with user consent management. However, no explicit privacy policy or terms of service pages were found, and WHOIS data for the domain is unavailable, which raises some concerns about domain registration transparency. Security posture is generally good with HTTPS enforced and secure form handling, but the absence of visible security headers and lack of published security or incident response policies suggest room for improvement. No vulnerabilities or exposed sensitive data were detected in the provided content. Overall, the website is safe, professional, and trustworthy, but the missing WHOIS data and privacy documentation slightly reduce the trust score. Recommendations include adding explicit privacy and terms of service pages, publishing security policies and incident response contacts, implementing security headers, and verifying domain registration details to enhance trust and compliance.
 Berounský Region
berounskyregion.cz
Media · Czech Republic
60Medium
NIS2 17 · GDPR 10
NIS2 17 · GDPR 10
Berounský Region is a regional media portal focused on culture and social life in the Beroun area of the Czech Republic. It provides news, event invitations, calendars, videos, and features on regional personalities, targeting residents and visitors interested in local cultural activities. The website is built on WordPress with common plugins and integrates Google Analytics for user tracking. It is mobile-optimized and regularly updated with relevant content. Security posture is moderate with HTTPS enabled but lacks some security headers and formal privacy/cookie policies. WHOIS data is unavailable, which slightly reduces trust but the active social media presence and content quality support legitimacy. Overall, the site serves as a valuable regional cultural information source with room for improvement in privacy compliance and security practices.
 Bezplatná právní poradna online zdarma pro všechny
bezplatnapravniporadna.cz
Other · Czech Republic
48High
NIS2 17 · GDPR 40
NIS2 17 · GDPR 40
Bezplatná právní poradna online zdarma pro všechny is a Czech Republic-based free legal advice website offering extensive legal content authored by legal professionals. The site targets the general public seeking legal guidance without charge, positioning itself as a comprehensive resource for various legal topics including family law, civil law, labor law, and more. The business model revolves around providing free legal information and advice, supported by advertising revenue from Google Adsense and Czech Sklik networks. The website demonstrates consistent branding and good content quality with a professional and user-friendly design.
 European Business Enterprise, a.s.
statnisprava.cz
Government · Czech Republic
61Medium
NIS2 22 · GDPR 25
NIS2 22 · GDPR 25
The website statnisprava.cz is a Czech government-related public service portal operated by European Business Enterprise, a.s. It provides comprehensive information on government offices, job vacancies, tenders, insolvencies, and related public services. The site targets a broad audience including citizens seeking official information and services. Technically, the site uses IBM Domino backend technology with a frontend built on HTML5, Bootstrap, jQuery, and Font Awesome, delivering a responsive and navigable user experience. Security posture is moderate with HTTPS usage and no visible sensitive data exposure, but lacks advanced security headers and explicit cookie consent mechanisms. WHOIS data is unavailable, which slightly reduces trust but the business information and content quality support legitimacy. Overall, the site is professional, content-rich, and serves an essential government function with room for security and privacy improvements.
 Městské kulturní centrum Hořovice
mkc-horovice.cz
Government · Czech Republic
41High
NIS2 17 · GDPR 25
NIS2 17 · GDPR 25
Městské kulturní centrum Hořovice (MKC) is a local government cultural institution based in Hořovice, Czech Republic, founded in 2009. It offers a variety of cultural services including event hosting, exhibitions, library services, and tourist information. The website serves as a portal for community engagement, event calendars, and cultural promotion, targeting local residents and tourists. MKC maintains a consistent brand presence with clear contact information and social media integration primarily via Facebook. Technically, the site is built on WordPress with modern plugins for SEO, sliders, and search functionality, demonstrating a moderate to good level of digital maturity.
 Openplace s.r.o.
nafialce.cz
Hospitality · Czech Republic
74Medium
NIS2 2 · GDPR 100
NIS2 2 · GDPR 100
Na Fialce is a small hospitality and cultural center located in Říčany near Prague, operated by Openplace s.r.o. The center caters to sports enthusiasts, film lovers, and fans of quality food and coffee, offering a variety of services including sports facilities, cultural events, cinema, and dining options. The website presents a professional and consistent brand image with good content quality and user experience. Technically, the site uses modern web technologies such as Bootstrap, Google Tag Manager, Facebook Pixel, and Cookiebot for cookie consent management. However, the absence of WHOIS data and explicit privacy and terms policies limits full trust verification. Security posture is moderate with HTTPS usage and cookie consent but lacks visible security headers and detailed security policies. Overall, the site is safe for general audiences and demonstrates a moderate level of digital maturity.
 Hotel zámek Berchtold
zamekberchtold.cz
Hospitality · Czech Republic
63Medium
NIS2 17 · GDPR 25
NIS2 17 · GDPR 25
Hotel zámek Berchtold is a hospitality business located in the Czech Republic offering a range of services including corporate events, teambuilding, weddings, family vacations, wellness, sports, and restaurant facilities. The website presents a professional and consistent brand image with clear navigation and relevant content targeting corporate clients, families, and tourists. The business is small-sized and has been established since 2006, supported by a domain registration consistent with its history. Technically, the website is built on WordPress hosted on WordPress.com, leveraging Jetpack and other standard plugins. It uses HTTPS with good SSL configuration and includes integrations such as Facebook SDK and Google Translate. Performance and mobile optimization are moderate to good, though accessibility features could be improved. From a security perspective, the site benefits from WordPress.com hosting security but lacks explicit security policies, vulnerability disclosure, and advanced security headers. Privacy compliance is partial, with a cookie consent mechanism present but no dedicated privacy policy or terms of service pages. Contact information is comprehensive and trustworthy. Overall, the website is safe, professional, and credible with minor gaps in privacy and security documentation. Strategic improvements in privacy policy publication, security headers, and incident response information would enhance trust and compliance.
 Olivova dětská léčebna o.p.s.
olivovna.cz
Healthcare · Czech Republic
57Medium
NIS2 2 · GDPR 40
NIS2 2 · GDPR 40
Olivova dětská léčebna o.p.s. is a well-established non-profit pediatric healthcare organization based in Říčany u Prahy, Czech Republic. Founded in 1896, it provides comprehensive inpatient treatment and rehabilitation services for children aged 1 to 18 years, fully covered by public health insurance. The organization focuses on treating respiratory and musculoskeletal diseases, childhood obesity, and related conditions, emphasizing prevention and follow-up care. The website reflects a professional and trustworthy presence with clear service offerings and engagement channels for parents, children, and medical professionals. Technically, the website is built on the SKY:CMS platform and employs modern web technologies including asynchronous JavaScript loading, Google Tag Manager, Google Analytics, Microsoft Clarity, and Facebook Pixel for analytics and marketing. The site is mobile-optimized, accessible, and SEO-friendly, with a cookie consent mechanism compliant with GDPR. However, explicit security headers are not fully implemented, and no dedicated security or incident response policies are published. Security posture is solid with HTTPS enforced and no visible vulnerabilities or exposed sensitive data. The absence of WHOIS data due to privacy protection slightly reduces transparency but is understandable for a healthcare non-profit. Overall, the site demonstrates a mature digital presence with good privacy compliance and user engagement, though improvements in security headers and incident response transparency are recommended. The risk assessment is low, with no signs of malicious activity or content safety concerns. Strategic recommendations include enhancing security headers, publishing security policies, and maintaining regular audits of third-party scripts to ensure ongoing compliance and security.
- Kynologický klub Lety
kklety.cz
Other · Czech Republic
50Medium
NIS2 17 · GDPR 25
NIS2 17 · GDPR 25
Kynologický klub Lety is a small, local dog training club based in the Czech Republic, offering a variety of dog training courses including socialization for puppies, basic obedience, rally obedience, and protection training. The website serves as an information hub for members and interested dog owners, providing event updates, photo galleries, and contact information. The club appears to be community-focused with active engagement through social media and email subscriptions. Technically, the website uses a custom CMS with JavaScript libraries such as jQuery and MooTools. It includes cookie consent mechanisms and privacy policy pages, indicating compliance with GDPR. However, there is no evidence of advanced security headers or incident response policies. The site is moderately optimized for performance and accessibility but could benefit from improvements in mobile responsiveness and security hardening. From a security perspective, the site uses HTTPS (assumed from standard practice though not explicitly confirmed), has cookie consent, and no visible vulnerabilities in the HTML content. The lack of WHOIS data is a concern for domain legitimacy and trust but does not directly impact the website's operational security. Overall, the site is safe for general audiences and does not contain any adult or questionable content. Strategically, the club should verify domain registration details and enhance security posture by implementing security headers and publishing incident response information. Improving mobile optimization and SEO could also enhance user experience and reach.
- SSpolek RC Leťánek z.s.
letanek.cz
Non-profit · Czech Republic
44High
NIS2 2 · GDPR 10
NIS2 2 · GDPR 10
Leťánek.cz is the website of Spolek RC Leťánek z.s., a small non-profit family center based in the Czech Republic, founded in 2009. The organization focuses on providing community and recreational activities for families, parents, and children, including events like the Pohádkový les. The website serves as an informational portal with basic content about upcoming events and organizational details. Technically, the site uses legacy technologies such as jQuery 1.3.2 and Google Analytics for tracking, but lacks modern CMS or frameworks. The site is accessible over HTTPS but lacks advanced security headers and cookie consent mechanisms, which are important for GDPR compliance. The website is not mobile optimized and has basic SEO and accessibility features. No contact emails or phone numbers are directly visible on the main page, which limits direct communication channels. The domain registration data is consistent with the organization's profile and shows a long-standing presence since 2009, supporting legitimacy.
 Ekoregion Úhlava
ekoregion-uhlava.cz
Non-profit · Czech Republic
55Medium
NIS2 2 · GDPR 10
NIS2 2 · GDPR 10
Ekoregion Úhlava is a small non-profit organization focused on regional development and community support in the Úhlava region of the Czech Republic. The website serves as a platform to disseminate information about grant programs, local initiatives, and educational events. It targets local residents, non-profit organizations, and small businesses. The organization appears to be well-established with a domain registered since 2004 and supported by EU funds. Technically, the website is built on Drupal 8 with standard web technologies and uses Google Analytics for visitor tracking. However, it lacks visible privacy and cookie policies, which is a compliance gap. Security posture is moderate with HTTPS usage but no detected security headers or vulnerability disclosures. Overall, the site is functional, content-rich, and safe for general audiences but could improve in privacy compliance and security best practices.
- SSvazek obcí mikroregionu Kněževes
knezevesko.cz
Government · Czech Republic
50Medium
NIS2 17 · GDPR 25
NIS2 17 · GDPR 25
Svazek obcí mikroregionu Kněževes is a small regional municipal association in the Czech Republic focused on promoting local culture, tourism, and community information. The website provides detailed content about local history, events, and official notices, targeting residents and visitors interested in the Kněževes microregion. The business model is non-profit and government-oriented, with a clear focus on community engagement and cultural heritage. Technically, the website uses a custom CMS with JavaScript libraries such as jQuery and Highslide for interactive content. The site is moderately optimized for performance and accessibility, with basic mobile responsiveness and SEO practices. Cookie consent is implemented, indicating some privacy awareness, but there is room for improvement in security headers and explicit privacy policies. Security posture is moderate; HTTPS is used but no security headers were detected in the provided data. No vulnerabilities or exposed sensitive data were found, but the absence of WHOIS data reduces transparency and trust. The site lacks explicit contact information and security incident response details, which could be improved to enhance user trust and compliance. Overall, the website is functional and professional for its purpose but would benefit from enhanced security practices, clearer privacy and contact information, and improved transparency regarding domain registration details.


