Medium-risk security reports
99,068 public Guard scan reports. Each shows the site’s score, risk level and indicative NIS2 / GDPR posture from public signals.
Across the directory
All scanned sites, all time
- Websites scanned
- 150,179001234567890012345678900123456789,001234567890012345678900123456789
- Average score
- 600012345678900123456789/of100001234567890012345678900123456789
- High or critical risk
- 25%0012345678900123456789%
- Countries
- 112001234567890012345678900123456789
17,751–17,800 of 99,068
 Tennis Deutschland · tennisnet.com
tennisnet.com
Media · Germany
51Medium
NIS2 17 · GDPR 58
NIS2 17 · GDPR 58
The website tennisnet.com is a German-language sports news platform specializing in tennis coverage, including ATP and WTA news, live scores, and tournament updates. It targets tennis enthusiasts primarily in Germany and operates on the TYPO3 CMS platform, integrating various advertising and tracking technologies such as Google Analytics, Google Tag Manager, Facebook Pixel, and Google Adsense. The technical infrastructure is modern and supports mobile optimization, though performance is moderate. Security posture is generally good with HTTPS enabled, but lacks some security headers and explicit privacy and cookie policies. The absence of WHOIS data raises questions about domain registration legitimacy, though the website content and design appear professional and trustworthy. Overall, the site is functional and relevant to its audience but would benefit from enhanced privacy compliance and clearer business contact information.
- Transports Brevet
brevet.fr
Transportation · France
53Medium
NIS2 2 · GDPR 10
NIS2 2 · GDPR 10
Transports Brevet is a well-established French transportation company specializing in the logistics and transport of fresh and frozen products nationwide. Founded in 1966, it operates multiple logistics platforms and offers professional transport and storage services tailored to business clients. The website reflects a medium-sized enterprise with a clear focus on transportation and logistics within France. Technically, the site is built on Joomla CMS with modern front-end libraries such as Bootstrap and jQuery, and it includes Google Analytics for visitor tracking. The site is mobile-optimized and presents a professional design with clear navigation and relevant content. Security-wise, the site uses HTTPS and implements a cookie consent banner, but lacks visible security headers and explicit security or incident response policies. The absence of WHOIS registration data is a notable gap, limiting domain trust verification. Overall, the website is functional, professional, and safe for general audiences, but could improve in security transparency and compliance documentation.
 Groupe Sobotram
sobotram.fr
Transportation · France
56Medium
NIS2 2 · GDPR 25
NIS2 2 · GDPR 25
Groupe Sobotram is a well-established French transport and logistics company specializing in general goods and hazardous materials transport, operating both nationally and internationally. Founded in 1953 and acquired by Groupe Blondel in 2023, it maintains strategic locations including a SEVESO high-threshold site. The website reflects a professional business presence with clear service offerings and subsidiary information. Technically, the site uses modern web technologies such as Bootstrap, Mapbox GL JS, and Vimeo API, providing a good user experience with mobile optimization and structured navigation. Security posture is moderate with HTTPS implied but lacks explicit security headers and published security policies. Privacy compliance is basic with a privacy policy present but no cookie consent mechanism. Overall, the domain registration data supports the legitimacy and trustworthiness of the business.
 BTL Transports et Logistique
btl-i.fr
Transportation · France
60Medium
NIS2 17 · GDPR 25
NIS2 17 · GDPR 25
BTL Transports et Logistique is a well-established French transport and logistics company with a rich history dating back to 1852, formally created in its current form in 2008 through the merger of five regional companies. The company operates primarily in northern France with three main agencies and offers a range of services including transport, logistics, freight forwarding, parcel pickup points, and vehicle covering. Their market position is that of a trusted regional player with a commitment to environmental responsibility and customer satisfaction. Technically, the website employs modern frameworks such as Bootstrap and jQuery, with good mobile optimization and a professional design. Security-wise, the site uses HTTPS and has a cookie consent mechanism but lacks advanced security headers and explicit privacy or security policies. The absence of WHOIS data limits full trust verification, but the website content and business information appear consistent and professional. Overall, the site presents a solid digital presence with room for improvement in security and privacy transparency.
- Groupe Bernardi
bernardi-logistique.fr
Transportation · France
54Medium
NIS2 2 · GDPR 10
NIS2 2 · GDPR 10
Groupe Bernardi is a well-established French transportation and logistics company founded in 1961, specializing in national and international freight transport, storage, and distribution services. The company leverages its membership in the ASTRE network to extend its market reach and offers a variety of services including palletized freight, bulk transport, and logistics solutions. Their digital presence includes an online booking platform and client portals, reflecting a moderate level of digital maturity. Technically, the website is built on the SPIP CMS with modern web technologies such as Bootstrap and JavaScript libraries. It features responsive design and good SEO practices, although some accessibility features could be improved. The site uses HTTPS and includes GDPR-compliant cookie consent mechanisms, indicating attention to privacy and security. From a security perspective, the website demonstrates good practices such as HTTPS enforcement and cookie consent but lacks explicit security policies and incident response contacts. No critical vulnerabilities or exposed sensitive data were detected. The WHOIS data is consistent with the business claims, supporting the legitimacy of the domain and company. Overall, the website presents a professional and trustworthy image with solid business credibility and compliance. Strategic improvements in security headers and incident response transparency would further enhance their security posture.
 Transports Adam
transports-adam.com
Transportation · France
64Medium
NIS2 2 · GDPR 68
NIS2 2 · GDPR 68
Transports Adam is a French transport and logistics company based in Joinville, established in 1965. The company specializes in industrial road transport, exceptional transport, handling works, and storage services. The website presents a professional image with clear service offerings and contact options, including phone and social media. Technically, the site uses modern web technologies such as Bootstrap, Matomo analytics, and cookie consent management via tarteaucitron. The hosting is provided by OVH, a reputable registrar and hosting provider. Security posture is adequate with HTTPS enabled and cookie consent implemented, but lacks advanced security headers and DNSSEC. Privacy policies and terms of service are not explicitly found, indicating room for compliance improvement.
 Manitou
manitou.com
Manufacturing · France
69Medium
NIS2 17 · GDPR 35
NIS2 17 · GDPR 35
Manitou is a well-established French manufacturing company specializing in handling, lifting, and earthmoving equipment for diverse sectors including agriculture, construction, and industries. With over 60 years of experience, the company offers a broad range of machinery such as telehandlers, forklift trucks, and aerial work platforms, complemented by attachments and services like financing and maintenance. The website reflects a mature global brand with extensive multilingual support and a professional digital presence. Technically, the website is built on Drupal 10, leveraging modern web technologies including Google Tag Manager and Matomo for analytics. The site is mobile-optimized, accessible, and SEO-friendly, providing a good user experience. Security posture is solid with HTTPS enforced and cookie consent mechanisms in place, though there is room for improvement in security headers and incident response transparency. The WHOIS data is notably missing, which reduces transparency but is likely due to privacy protection services. Despite this, the website's professional content, structured data, and social media presence support its legitimacy. No WAF or blocking mechanisms were detected, allowing full content access. Overall, Manitou's website demonstrates strong business credibility and technical maturity, with minor security and transparency gaps that can be addressed to enhance trust and compliance.
 Anaveo
anaveo.fr
Technology · France
70Medium
NIS2 17 · GDPR 10
NIS2 17 · GDPR 10
Anaveo is a leading French company specializing in intelligent electronic security solutions, offering a comprehensive range of services including video surveillance, access control, intrusion detection, fire safety, and unified security platforms. The company targets various sectors such as retail, industry, healthcare, hospitality, and urban mobility, positioning itself as a key player in the French security technology market. Their business model focuses on delivering innovative, integrated security applications and smart business tools to enhance safety and operational efficiency for enterprises. Technically, the website is built on a modern WordPress platform using Elementor and Yoast SEO, with advanced analytics and tracking tools such as Google Analytics, Google Tag Manager, LinkedIn Insight, and Rollbar for error monitoring. The site demonstrates excellent performance, mobile optimization, and SEO practices, reflecting a mature digital infrastructure. Security measures include HTTPS, reCAPTCHA, and cookie consent management, although explicit security headers and policies could be improved. From a security posture perspective, the site shows good practices with no evident vulnerabilities or exposed sensitive data. However, the absence of WHOIS registration details and explicit privacy and security policies slightly reduce trustworthiness. The site holds APSAD certifications, reinforcing its credibility in the security industry. Overall, Anaveo presents a professional, trustworthy online presence with strong business credibility and technical maturity. To enhance security and compliance, it is recommended to publish clear privacy and security policies, improve WHOIS transparency, and implement additional security headers. These steps will further solidify trust and regulatory compliance, supporting Anaveo's market leadership and customer confidence.
 Berner
berner.com
Manufacturing · United States
68Medium
NIS2 2 · GDPR 88
NIS2 2 · GDPR 88
Berner is a well-established manufacturer specializing in air curtains and air doors, serving commercial and industrial markets primarily in the United States. The company positions itself as a leading North American manufacturer with a focus on energy savings, indoor air quality, and sustainable solutions. Their website reflects a mature digital presence with comprehensive product information, technical support, and customer engagement tools. Technically, the site is built on WordPress with modern frameworks like Bootstrap and integrates advanced marketing and analytics tools such as Google Tag Manager, Hotjar, and Adobe Analytics. Security posture is strong with HTTPS enforced and a robust cookie consent mechanism, although some security headers could be improved. Privacy compliance is well addressed with clear policies and granular cookie controls. Overall, the website demonstrates high professionalism, trustworthiness, and business credibility, supported by consistent WHOIS data and domain age.
 Getswish AB
swish.com
Finance · Sweden
71Medium
NIS2 2 · GDPR 35
NIS2 2 · GDPR 35
Getswish AB operates the Swish mobile payment service, a widely adopted real-time payment platform in Sweden since 2012. The company targets both consumers and businesses, offering fast, secure payments authenticated via Mobile BankID. The website reflects a mature digital presence with modern technologies such as Vue.js and Contentful CMS, optimized for mobile users. Security posture is strong with HTTPS and secure payment authentication, though some security headers and incident response details are missing. The absence of WHOIS data for the domain introduces some uncertainty about domain registration transparency, but the professional website and business information support legitimacy. Overall, the risk is moderate with recommendations to enhance security headers, privacy compliance, and domain registration transparency.
 WiiSmile
wiismile.com
Other · France
62Medium
NIS2 17 · GDPR 25
NIS2 17 · GDPR 25
WiiSmile is a French company founded in 2017 that provides externalized employee committee services tailored for small and medium enterprises (TPE & PME). Their business model focuses on enhancing employee benefits and quality of life by aggregating offers typically found in larger company committees. The website positions WiiSmile as a niche player offering meal vouchers, gift checks, team building, and other employee engagement services. The target audience is primarily small business owners and their employees in France. The company maintains a professional online presence with clear branding and trust signals such as embedded Google and Trustpilot reviews.
- Brittany Ferries
brittany-ferries.com
Transportation · United Kingdom
66Medium
NIS2 2 · GDPR 53
NIS2 2 · GDPR 53
Brittany Ferries operates as a well-established ferry transportation and holiday package provider linking the UK, Ireland, France, Spain, and Portugal. The company targets travelers seeking ferry routes and holiday accommodations in these countries, maintaining a strong market position with a domain age dating back to 1996. The website presents localized versions for different countries, enhancing user experience for diverse audiences. Technically, the site uses Cloudflare DNS and Google Tag Manager for analytics, with moderate performance and good mobile optimization. Security posture is adequate with HTTPS and asynchronous tag loading but lacks advanced security headers and DNSSEC. Privacy compliance is partial with a privacy policy present but no cookie consent mechanism or terms of service visible. Overall, the site is professional, trustworthy, and content is safe for general audiences.
 Guémas Immopro
guemas.fr
Real Estate · France
62Medium
NIS2 17 · GDPR 10
NIS2 17 · GDPR 10
Guémas Immopro is a French real estate company specializing in commercial properties such as offices, activity spaces, and parking in cities including La Rochelle, Paris, and Bordeaux. The website is professionally designed using the Wix platform, featuring modern web technologies and a cookie consent mechanism via Usercentrics, indicating some level of GDPR compliance. However, the absence of explicit privacy and terms of service pages and lack of visible contact information limit transparency. The WHOIS data for the domain is unavailable, which raises concerns about domain registration legitimacy and age, especially given the company's claim of 30 years in business. Security posture is moderate with HTTPS implied but no detected security headers or advanced protections. Overall, the website presents a professional front but would benefit from enhanced transparency and security measures.
 betaITS GmbH
beta-its.de
Technology · Germany
68Medium
NIS2 10 · GDPR 33
NIS2 10 · GDPR 33
betaITS GmbH is a small German managed IT services provider specializing in modern, simple, and customer-friendly IT solutions. Their offerings include managed endpoint services, infrastructure management, Microsoft 365 management, security, backup, and hardware procurement. The company targets businesses seeking comprehensive IT management with a focus on proactive service and operational continuity. The website is professionally designed using modern technologies like Astro, with excellent mobile optimization and clear navigation. Security posture is good with HTTPS enforced and no visible vulnerabilities, though security headers and explicit security policies could be improved. Privacy compliance is basic with a privacy policy present but no cookie consent mechanism detected. Contact is primarily via Calendly and social media, with no direct emails or phone numbers visible. Overall, the site is trustworthy, well-branded, and content-rich, supporting betaITS GmbH's market position as a reliable managed IT service provider.
 TC Expo
tcexpo.uz
Other · Uzbekistan
60Medium
NIS2 2 · GDPR 35
NIS2 2 · GDPR 35
TC Expo is a newly established company (founded in 2024) specializing in exhibition stand design and construction, targeting businesses and organizations that require professional exhibition architecture services. The company positions itself as a leading provider in its sector with international partnerships and a focus on customized, high-quality solutions. The website is built on the Tilda CMS platform, leveraging modern web technologies and CDN hosting for performance and reliability. The site is well-designed, mobile-optimized, and provides a good user experience, although it lacks explicit privacy and cookie policies as well as clear contact information. Security posture is adequate with HTTPS enabled but could be improved by adding security headers and incident response contacts. Overall, the website is professional and trustworthy but would benefit from enhanced privacy compliance and security transparency.
- Iictashkent.com | 502: Bad gateway
ictashkent.com
Other
71Medium
NIS2 2 · GDPR 35
NIS2 2 · GDPR 35
The website ictashkent.com is currently inaccessible due to a 502 Bad Gateway error served via Cloudflare, indicating an origin server failure. The page content is limited to an error message with no business or contact information, policies, or services described. This prevents a full assessment of the company's business operations, market position, or technical infrastructure. The only technology detected is Cloudflare acting as a proxy and WAF. Security posture is weak due to lack of security headers and absence of privacy or cookie policies. No forms, scripts, or analytics are present to evaluate data collection or user tracking. Overall, the site is non-functional and provides no trust or credibility signals.
 Central Asian Expo Uzbekistan
caexuzbekistan.com
Real Estate · Uzbekistan
51Medium
NIS2 2 · GDPR 35
NIS2 2 · GDPR 35
CAEx Uzbekistan is a modern international exhibition center located in Tashkent, Uzbekistan, serving as a major business arena in Central Asia. It offers versatile pavilion spaces adaptable for various projects and event formats. The center is a member of prestigious international exhibition associations UFI and IAEE, underscoring its commitment to quality and international standards. The website targets businesses and event organizers seeking exhibition and event hosting services in the region. Technically, the website employs modern web technologies including Swiper.js for interactive galleries, AOS for animations, Google Tag Manager and Yandex Metrika for analytics, and a live chat widget for customer engagement. The site is hosted behind Cloudflare DNS and CDN services, ensuring reliable performance and security. The design is professional, mobile-optimized, and provides clear navigation and relevant content. From a security perspective, the site uses HTTPS with a valid SSL certificate and has domain transfer protections enabled. However, DNSSEC is not enabled, and no explicit security headers were detected, which are areas for improvement. Privacy compliance is basic, with a privacy policy present but no cookie consent mechanism or GDPR-specific disclosures. Contact information is clearly provided, but no incident response or vulnerability disclosure policies are available. Overall, the website presents a trustworthy and professional image suitable for its business purpose. Strategic improvements in security headers, DNSSEC, and privacy compliance would enhance its security posture and regulatory adherence.
- Centrum Air
centrum-air.com
Transportation · Uzbekistan
60Medium
NIS2 22 · GDPR 70
NIS2 22 · GDPR 70
Centrum Air is a private airline company based in Uzbekistan, founded in 2023, offering affordable flight tickets primarily from Tashkent to various regional and international destinations. The website provides a modern booking platform built on Next.js and React, featuring multiple flight routes, schedules, and additional services such as extra baggage, seat selection, and wheelchair rental. The technical infrastructure is contemporary with moderate performance and good mobile optimization. Security posture is adequate with HTTPS enabled and domain transfer protection, but lacks DNSSEC and security headers. Privacy compliance is weak due to absence of privacy and cookie policies. Overall, the business appears legitimate and focused on transportation services with a clear market presence in Uzbekistan and surrounding regions.
 O'zbekiston Savdo-sanoat palatasi
chamber.uz
Government · Uzbekistan
59Medium
NIS2 17 · GDPR 35
NIS2 17 · GDPR 35
The website represents the Chamber of Commerce and Industry of Uzbekistan, a key governmental institution supporting trade and industry sectors within Uzbekistan. It provides services such as trade facilitation, business registration, and information dissemination to businesses and government entities. The domain is well-established since 2007, reflecting a mature presence in the market. Technically, the site uses modern frontend frameworks like Bootstrap and Vue components, ensuring a responsive and professional user experience. However, there is a lack of explicit privacy and cookie policies, and no visible security headers, which are areas for improvement. The security posture is moderate, with no detected vulnerabilities but missing best practices. Overall, the site is trustworthy and professional but would benefit from enhanced privacy compliance and security measures.
 Komtrans Tashkent + Futuroad Expo Tashkent
comtrans.uz
Transportation · Uzbekistan
52Medium
NIS2 2 · GDPR 35
NIS2 2 · GDPR 35
Komtrans Tashkent + Futuroad Expo Tashkent is a newly established international exhibition platform focused on cargo and commercial transport in Uzbekistan and Central Asia. The website serves as a B2B platform for showcasing products, technologies, and solutions in the commercial transport sector. The event is positioned as a leading regional exhibition with a professional digital presence built on the Tilda CMS platform. The technical infrastructure includes modern web technologies and integration with Google Tag Manager for analytics. Security posture is adequate with HTTPS enabled, but lacks advanced security headers and formal privacy and cookie policies, indicating room for improvement in compliance and security maturity. Overall, the website is functional, professionally designed, and trustworthy, with clear contact information and social media presence. Strategic recommendations include enhancing privacy compliance, implementing security headers, and publishing incident response policies to strengthen trust and security posture.
Transportation · Uzbekistan
64Medium
NIS2 2 · GDPR 35
NIS2 2 · GDPR 35
Tashkent International Auto Show (TIAS) is a regional automotive exhibition event based in Uzbekistan, targeting automotive manufacturers, dealers, and lifestyle consumers in Central Asia. The website presents the event professionally with detailed information about the exhibition, participation, and partner programs. The technical infrastructure is built on the Tilda CMS platform, leveraging modern JavaScript libraries and third-party integrations such as Google Tag Manager and Facebook Pixel for analytics and marketing. The site is mobile optimized and provides a good user experience with clear navigation and relevant content. Security posture is adequate with HTTPS enabled, but lacks visible security headers and formal privacy and cookie policies, which are compliance gaps. The domain registration data aligns well with the business purpose and location, indicating legitimacy. Overall, the website is a credible digital presence for the TIAS event but would benefit from enhanced privacy compliance and security best practices.
 Bundesverband BioEnergie e.V. (BBE)
fachverband-holzenergie.de
Energy · Germany
51Medium
NIS2 2 · GDPR 28
NIS2 2 · GDPR 28
Fachverband Holzenergie is a German industry association dedicated to promoting sustainable wood energy usage. It operates under the umbrella of Bundesverband BioEnergie e.V. (BBE) and provides advocacy, publications, events, and working groups to support the wood energy sector. The website is professionally designed, content-rich, and targets industry stakeholders, policymakers, and environmental advocates. The association holds a solid market position within Germany's renewable energy landscape, focusing on sustainable forestry and climate protection through wood energy. Technically, the website is built on the Concrete5 CMS platform, utilizing modern JavaScript libraries such as jQuery and LayerSlider for interactive content. The site is mobile-optimized with good navigation and accessibility features, although some accessibility aspects could be improved. Performance is moderate, with no critical technical issues detected. From a security perspective, the site enforces HTTPS and implements a cookie consent mechanism compliant with GDPR. However, it lacks explicit security headers and does not provide visible security policies or incident response contacts. No vulnerabilities or exposed sensitive data were found. Analytics are handled via Matomo, emphasizing privacy compliance with cookie opt-in. Overall, the website presents a trustworthy and professional front for the Fachverband Holzenergie association. Strategic improvements in security headers, incident response transparency, and accessibility would enhance its security posture and compliance. The domain WHOIS data is minimal but consistent with the website's German focus, supporting legitimacy. No WAF or blocking mechanisms interfere with content access.
 Bayerische Staatsforsten AöR
baysf.de
Government · Germany
72Medium
NIS2 2 · GDPR 68
NIS2 2 · GDPR 68
Bayerische Staatsforsten AöR is a publicly owned forestry organization under the Free State of Bavaria, managing the entire Bavarian state forest with a focus on sustainable, integrative forest management. The website reflects a mature digital presence with a professional design, clear navigation, and comprehensive content targeting citizens, forestry professionals, and environmental stakeholders. The organization offers a broad range of services including wood production, hunting, renewable energy, and nature conservation. Technically, the site is built on Drupal CMS, uses Matomo for analytics with user consent, and supports responsive design and accessibility. Security posture is strong with HTTPS enforced and cookie consent mechanisms, though explicit security headers and policies could be improved. Overall, the domain and WHOIS data align with the organization's government affiliation, supporting legitimacy and trust. No critical vulnerabilities or suspicious content were detected.
 Deutsche Säge- und Holzindustrie Bundesverband e. V.
zukunft-holz.de
Manufacturing · Germany
60Medium
NIS2 17 · GDPR 48
NIS2 17 · GDPR 48
The website 'Zukunft Holz' represents the Deutsche Säge- und Holzindustrie Bundesverband e. V., a well-established German industry association focused on sustainable wood usage and the sawmill sector. The organization acts as a key intermediary between forestry and wood processing industries, promoting climate protection, employment, and value creation. The site offers comprehensive information, press releases, event details, and project highlights, targeting industry stakeholders, policymakers, and interested public. Technically, the site is built on WordPress with a modern theme and plugins, including SEO and cookie consent tools, ensuring a professional digital presence. Security measures such as HTTPS, hCaptcha, and cookie consent are implemented, though additional security headers could enhance protection. The domain registration data aligns well with the business claims, indicating legitimacy and trustworthiness. Overall, the site is well-designed, content-rich, and compliant with GDPR, supporting the organization's mission effectively.
- b&s creations
bs-creations.ch
Technology · Switzerland
53Medium
NIS2 2 · GDPR 53
NIS2 2 · GDPR 53
b&s creations is a small Swiss-based service provider specializing in design, web design, and text content creation. The website presents basic information about their services and showcases client projects, targeting small to medium businesses or individuals seeking creative digital services. The technical infrastructure is based on CMSimple with older jQuery libraries and includes basic interactive elements such as sliders and cookie consent banners. Security posture is limited with no visible HTTPS confirmation or security headers, and no explicit contact emails or phone numbers are provided, relying on a contact form instead. Privacy compliance is addressed with a cookie consent mechanism and a privacy policy page in German. Overall, the website is functional but basic in design and security, with room for modernization and enhanced trust signals.
 Primus-Ofenshop.com
primus-ofenshop.com
Retail · Germany
68Medium
NIS2 17 · GDPR 88
NIS2 17 · GDPR 88
Primus-Ofenshop.com operates as a specialized e-commerce retailer focused on fireplaces, tiled stoves, and related accessories, targeting consumers in Germany. The company emphasizes professional consulting by stove masters and offers individual stove planning and handcraft services, positioning itself as a trusted regional expert with a broad product range and over 15,000 completed projects. The website is built on a modern WordPress and WooCommerce platform, leveraging Elementor for design and integrating trusted third-party services such as Trusted Shops and MonsterInsights for reviews and analytics. Cookie consent is managed via Cookiebot, reflecting attention to privacy compliance. Security posture is solid with HTTPS enforced and privacy-focused analytics settings, though the absence of explicit security headers and visible privacy policies indicates room for improvement. The lack of WHOIS data for the domain raises concerns about domain registration legitimacy, which should be verified to ensure trustworthiness. Overall, the site presents a professional and user-friendly experience with moderate risk due to incomplete compliance documentation and domain registration opacity.
 Stilbetten.de
stilbetten.de
Retail · Germany
67Medium
NIS2 2 · GDPR 88
NIS2 2 · GDPR 88
Stilbetten.de is a German e-commerce retailer specializing in beds and mattresses, offering a wide selection of quality products to consumers aiming to enhance their bedroom experience. The website is built on a modern WordPress platform using WooCommerce for e-commerce functionality and Elementor for design, hosted on Amazon AWS infrastructure. The site integrates advanced tracking and consent management tools such as Google Analytics, Microsoft Clarity, and Cookiebot, reflecting a moderate level of digital maturity. Security posture is solid with HTTPS enforced and privacy-conscious analytics configurations, although the absence of explicit privacy policies and terms of service pages indicates room for compliance improvement. Overall, Stilbetten.de presents a professional and trustworthy online retail presence with a focus on user experience and privacy-aware tracking.
- 비즈니스포스트 (Businesspost)
chwho.co.kr
Media · South Korea
60Medium
NIS2 2 · GDPR 35
NIS2 2 · GDPR 35
채널Who is a Korean economic media channel operated by CHANNELWHO, Inc., focusing on people-centered economic analysis and business news. The website offers video content, interviews, and news briefings targeting Korean-speaking business professionals and investors. The business is positioned as a niche media provider with a consistent brand and professional content. Technically, the site uses modern web technologies including Google Tag Manager and Analytics, with hosting likely on AWS infrastructure. Mobile optimization is good, and navigation is clear. Security posture is adequate with HTTPS and secure form handling, but lacks advanced security headers and explicit cookie consent mechanisms. WHOIS data is transparent and consistent with the business identity, supporting legitimacy. Overall, the site is professional and trustworthy with room for security and privacy improvements.
- 삼삼성청년SW·AI아카데미(SSAFY,싸피)
ssafy.com
Education · South Korea
60Medium
NIS2 17 · GDPR 35
NIS2 17 · GDPR 35
The website www.ssafy.com represents the Samsung Youth Software and AI Academy (SSAFY), a government-supported educational initiative focused on providing software and AI training to young job seekers in South Korea. The platform offers coding education, IT training, and employment support services, positioning itself as a key player in the national youth employment and technology education sector. The site content is primarily in Korean and targets youth preparing for careers in software and AI fields. Technically, the website employs legacy jQuery 1.11.0 and integrates Google Analytics for visitor tracking. The site loads asynchronously and uses NetFunnel for traffic management. However, the technical implementation is basic with limited modern frameworks or CMS detected. Mobile optimization and accessibility are at a basic level, and SEO practices are minimal but present through meta tags and Open Graph data. From a security perspective, the site lacks visible security headers and privacy or cookie policies, which are critical for compliance and user trust. The WHOIS data for the domain is unavailable, which raises concerns about transparency and domain legitimacy despite the active and professional nature of the website. No forms or user input fields are present on the homepage, reducing immediate attack surface but also limiting user engagement features. Overall, the website is functional and serves its educational purpose but requires improvements in privacy compliance, security best practices, and WHOIS transparency to enhance trustworthiness and regulatory adherence.
 비즈니스포스트
c-journal.co.kr
Media · South Korea
63Medium
NIS2 17 · GDPR 35
NIS2 17 · GDPR 35
C-journal is a Korean business media platform targeting CEOs and global business leaders, providing management insights and business news. The website positions itself as a leading Korean business media outlet, focusing on delivering valuable content to its target audience. The business is registered under the name 비즈니스포스트 with clear contact information and a physical address in Seoul, Korea. However, the domain WHOIS data shows a future creation date (2025), which is unusual and may indicate a data error or pre-registration status. Technically, the website uses a moderate technology stack including jQuery 1.12.4, vis-network, and Google Tag Manager for analytics. Hosting appears to be on Amazon AWS infrastructure. The site is mobile optimized with good SEO and basic accessibility features. Security headers are present but could be enhanced with stricter policies and updated libraries to improve security posture. Security-wise, the site enforces HTTPS and has a Content-Security-Policy header, but the Referrer-Policy is set to 'unsafe-url', which is not recommended. No critical vulnerabilities or exposed sensitive data were detected. Privacy and cookie policies are not explicitly found, which is a compliance gap. Overall, the site demonstrates a good security posture but has room for improvement in privacy compliance and security header implementation. The overall risk assessment is moderate with recommendations to update security headers, improve privacy disclosures, and verify domain registration details. The site is trustworthy and professional but should address the noted anomalies and compliance gaps to enhance credibility and security.
- KoreaWho
koreawho.com
Media · South Korea
68Medium
NIS2 17 · GDPR 53
NIS2 17 · GDPR 53
KoreaWho is a specialized media platform providing detailed biographical profiles and news about influential leaders in the Korean economy. The website targets business professionals, investors, and researchers interested in Korean corporate leadership. It offers a searchable database of profiles and news articles focusing on executives across various sectors including energy, finance, manufacturing, and transportation. The platform positions itself as a niche authoritative source for Korean business leadership information. Technically, the website employs modern web technologies such as jQuery, Google Tag Manager, and Google Fonts. It is mobile-optimized with good SEO practices and moderate performance. The site uses HTTPS and integrates analytics tools like Google Analytics and Naver Analytics, indicating a moderate level of digital maturity. From a security perspective, the site enforces HTTPS but lacks comprehensive security headers and cookie consent mechanisms. No critical vulnerabilities or exposed sensitive data were detected. Privacy compliance is basic, with a privacy policy present but no explicit GDPR compliance or cookie consent. Contact information is clearly provided, enhancing business credibility. Overall, the website presents a professional and trustworthy front with quality content and good user experience. However, the absence of WHOIS registration data raises concerns about domain legitimacy, warranting further verification. Security and privacy practices could be improved to enhance compliance and trustworthiness.
- 비비즈니스포스트
bpforum.net
Finance · South Korea
64Medium
NIS2 2 · GDPR 35
NIS2 2 · GDPR 35
The website bpforum.net serves as the official platform for the 2025 Business Post Finance Forum held in Hanoi, Vietnam, focusing on expanding Korea-ASEAN financial cooperation. Hosted by the Korean media company 비즈니스포스트, the site targets financial professionals, policymakers, and investors interested in ASEAN and Vietnamese financial markets. The business model centers on organizing specialized finance forums to facilitate networking and knowledge sharing. The site content is primarily in Korean with professional event details, speaker introductions, and partner information, reflecting a focused niche audience. Technically, the website employs a modern front-end stack including Bootstrap, jQuery, Owl Carousel, and Animate.css, hosted on AWS infrastructure. The site is mobile-optimized with good navigation and design quality, though SEO and accessibility features are basic. No CMS or advanced analytics tools are detected, indicating a relatively straightforward technical setup. From a security perspective, the domain uses clientTransferProhibited status but lacks DNSSEC and visible security headers, which are recommended for enhanced protection. The absence of privacy and cookie policies indicates compliance gaps, especially under GDPR. No incident response or vulnerability disclosure information is provided. WHOIS data is transparent and consistent with the business, supporting legitimacy. Overall, the site is professionally presented and credible for its business purpose but would benefit from improved security practices and privacy compliance to strengthen trust and regulatory adherence.
 sports4everybody
kitz-extremechallenge.com
Non-profit · Austria
53Medium
NIS2 2 · GDPR 53
NIS2 2 · GDPR 53
The website www.kitz-extremechallenge.com represents the World Extreme Run Challenge (WERC), an extreme sports event organized by the non-profit association sports4everybody. The event is held on the famous Kitzbühel Streif ski slope and aims to challenge participants with an up-and-down mountain run. The business model is non-profit, focusing on community engagement and supporting Austrian sports talents. The website content is professionally presented in German, with clear navigation and relevant event information. The site is supported by multiple reputable partners and sponsors, enhancing its credibility. Technically, the website uses modern web technologies including HTML5, CSS3, JavaScript, and popular libraries such as jQuery and Owl Carousel. It employs Matomo analytics for user tracking with privacy considerations. The site is mobile-optimized and performs moderately well. However, no CMS or hosting provider details are explicitly detected. Security posture is good with HTTPS enforced and secure form handling, but lacks some security headers and incident response information. From a security and compliance perspective, the site includes a privacy policy and cookie consent mechanism compliant with GDPR. Contact information is clearly provided, but no terms of service or security policy documents are found. The WHOIS data for the domain is missing or unavailable, which raises concerns about domain legitimacy despite the professional website presence. No WAF or blocking mechanisms are detected, and the content is safe for general audiences. Overall, the website is a credible and professional platform for the WERC event but should address WHOIS transparency and enhance security headers and policies to improve trust and compliance.
 Bundesministerium für Wohnen, Kunst, Kultur, Medien und Sport (BMWKMS)
sportministerium.at
Government · Austria
67Medium
NIS2 17 · GDPR 68
NIS2 17 · GDPR 68
The website www.bmwkms.gv.at represents the official online presence of the Austrian Federal Ministry for Housing, Arts, Culture, Media, and Sports (BMWKMS). It serves as a comprehensive information and service portal for citizens, cultural professionals, sports organizations, and media stakeholders in Austria. The ministry provides extensive resources including policy updates, funding opportunities, publications, and contact information. The site is well-branded, professionally designed, and clearly targeted at a broad public audience with interests in government services related to culture, sports, media, and housing. Technically, the website employs modern web standards including HTML5, CSS3, and JavaScript, with Bootstrap framework elements indicating responsive design. It uses eTracker for analytics, integrated with a cookie consent mechanism ensuring GDPR compliance. The site is mobile-optimized and accessible, with clear navigation and structured content. Hosting details are not explicitly disclosed, but HTTPS is enforced with a strong SSL configuration. From a security perspective, the site demonstrates good practices such as HTTPS usage and cookie consent. However, explicit security headers like Content-Security-Policy and X-Frame-Options are not visible in the provided data, and no published security policy or incident response contacts were found. No vulnerabilities or exposed sensitive data were detected. The domain WHOIS data aligns with the Austrian government entity, confirming legitimacy and trustworthiness. Overall, the website is a high-quality, trustworthy government portal with strong privacy and compliance posture. Strategic recommendations include enhancing security headers, publishing a security policy, and adding vulnerability disclosure information to further strengthen security and transparency.
 Stiftung Ehrenkodex
ehrenkodex.ch
Non-profit · Switzerland
71Medium
NIS2 2 · GDPR 68
NIS2 2 · GDPR 68
Stiftung Ehrenkodex operates as a Swiss nonprofit foundation providing a certification and quality seal for nonprofit organizations with Christian values. Their service focuses on ensuring transparency, ethical governance, and effective use of donations. The organization is well-positioned in the Swiss nonprofit sector, leveraging academic models from the University of Basel to underpin their certification process. Their website reflects a professional and trustworthy image, targeting nonprofit organizations and donors seeking assurance of ethical practices. Technically, the website is built on the Webflow platform, utilizing modern web technologies including Google Tag Manager for analytics and Finsweet Cookie Consent for privacy compliance. The site is mobile-optimized, fast-loading, and accessible, with clear navigation and comprehensive content. Security measures such as HTTPS and standard security headers are in place, though explicit security policies and incident response information are not publicly detailed. The security posture is strong with no evident vulnerabilities or exposed sensitive data. Privacy compliance is well-handled with a clear privacy policy and cookie consent mechanism. Contact information is transparent and includes multiple channels, enhancing business credibility. Overall, the site scores highly on content quality, technical implementation, security, privacy, and business credibility, making it a reliable and professional digital presence for the foundation. Strategically, the foundation should consider publishing explicit security and incident response policies to further enhance trust and compliance. Additionally, implementing a vulnerability disclosure policy and security.txt file would align with best practices. These steps would strengthen their security posture and demonstrate commitment to transparency and user protection.
 Bundes-Sport GmbH
austrian-sports.at
Government · Austria
68Medium
NIS2 2 · GDPR 73
NIS2 2 · GDPR 73
Bundes-Sport GmbH is a government-affiliated non-profit organization in Austria, established in 2018 to promote and manage funding for sports associations and institutions under the Bundes-Sportförderungsgesetz 2017. The organization plays a pivotal role in supporting both elite and grassroots sports through funding allocation, control, and evaluation. The website reflects a professional and consistent brand presence, targeting sports entities and stakeholders within Austria. Technically, the site is built on WordPress with modern plugins like Elementor and Revolution Slider, ensuring a good user experience and mobile optimization. Security posture is solid with HTTPS and cookie consent mechanisms, though some security headers could be improved. Privacy compliance is strong with a comprehensive privacy policy and cookie management. No critical vulnerabilities or suspicious content were detected, and WHOIS data confirms the legitimacy and consistency of the domain registration. Overall, the site demonstrates a mature digital presence suitable for its governmental and non-profit role.
 100% SPORT
safesport.at
Non-profit · Austria
56Medium
NIS2 2 · GDPR 33
NIS2 2 · GDPR 33
SAFE SPORT is a specialized non-profit initiative under the parent organization 100% SPORT, focused on creating safe and inclusive sports environments in Austria. The website offers educational services including e-learning, prevention, intervention, and support through the trusted partner vera* Sport. The platform targets sports officials, trainers, athletes, and guardians, providing resources and a network to promote sports safety. Technically, the website is built on WordPress with a modern theme and plugins supporting learning management and SEO, indicating a mature digital infrastructure. Security posture is good with HTTPS and cookie consent mechanisms, though it lacks explicit security policies and incident response details. Overall, the site is professional, trustworthy, and compliant with GDPR, serving a niche but important role in Austrian sports safety.
 Genderkompetenz im Sport
genderkompetenz-sport.at
Other · Austria
55Medium
NIS2 2 · GDPR 28
NIS2 2 · GDPR 28
Genderkompetenz im Sport is a specialized Austrian platform dedicated to promoting gender competence within the sports sector. It operates as a non-profit educational and advocacy entity affiliated with the parent organization 100% SPORT and supported by governmental bodies such as the Austrian Federal Ministry (BMKOES). The website offers resources, guidelines, networking opportunities, and event information aimed at sports organizations, trainers, and gender equality advocates. Technically, the site is built on WordPress using the Avada theme and Fusion Builder, with modern plugins like Slider Revolution, ensuring a professional and responsive user experience. Security posture is strong with HTTPS enforced and cookie consent mechanisms in place, although additional security headers could enhance protection. Privacy compliance is well addressed with a clear privacy policy and cookie consent banner. No critical vulnerabilities or suspicious patterns were detected. Overall, the website demonstrates a good balance of content quality, technical implementation, security, and business credibility, positioning it as a trustworthy resource in its niche.
- PPŸUR
pyur.com
Telecommunications · Germany
51Medium
NIS2 2 · GDPR 53
NIS2 2 · GDPR 53
PŸUR is a German telecommunications provider specializing in internet and TV services, targeting private customers, businesses, and housing industries. The website presents a professional and modern digital presence with clear service offerings and a strong market position as indicated by awards such as 'Testsieger bei connect'. The technical infrastructure leverages modern web technologies including React and Chakra UI, with integrated analytics and tag management tools from Google and Adobe. Security posture is solid with HTTPS enforcement and standard security headers, though explicit security policies and incident response information are not publicly detailed. The absence of WHOIS data limits full domain legitimacy verification but the overall business credibility remains high based on website content and branding.
- Bouldern gegen Krebs
bouldern-gegen-krebs.de
Non-profit · Germany
58Medium
NIS2 2 · GDPR 28
NIS2 2 · GDPR 28
Bouldern gegen Krebs is a German non-profit charity initiative organizing bouldering events to support cancer patients and related social projects. Founded in 2020 by Steffen Rieger, the organization leverages sport and community engagement to raise awareness and funds. The website is built on TYPO3 CMS and hosted by agenturserver, featuring a clean, professional design with good navigation and mobile optimization. Contact information and partner logos enhance credibility. However, the site lacks a cookie consent mechanism and visible security headers, indicating room for improvement in privacy and security compliance. No forms or tracking scripts were detected, suggesting minimal data collection and user tracking. Overall, the website is trustworthy and serves its niche audience effectively.
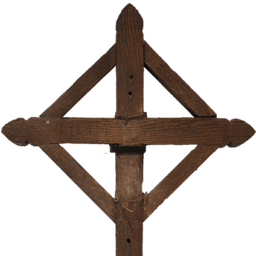 Cheltenham Civic Society
cheltenham-battlefield-crosses.org
Non-profit · United Kingdom
57Medium
NIS2 2 · GDPR 80
NIS2 2 · GDPR 80
Cheltenham Battlefield Crosses is a small non-profit museum dedicated to preserving and exhibiting WWI battlefield crosses commemorating fallen servicemen from Cheltenham. Managed by Cheltenham Civic Society, the museum offers historical insights and conservation efforts for these fragile artifacts. The website serves as an informative platform for visitors and researchers, providing stories and background on the crosses and soldiers. Technically, the site is built on WordPress with modern plugins for SEO and GDPR compliance, featuring a responsive design and basic accessibility. Security posture is good with HTTPS and cookie consent mechanisms, though improvements could be made by enabling DNSSEC and adding security headers. Overall, the site is trustworthy, well-branded, and professionally maintained, though it lacks explicit contact details and formal security policies.
 FID Verlag GmbH
gesundheitswissen.de
Healthcare · Germany
64Medium
NIS2 2 · GDPR 45
NIS2 2 · GDPR 45
Gesundheitswissen.de is a German health information portal operated by FID Verlag GmbH, providing expert-backed content on health, nutrition, natural medicine, and wellness. The site offers newsletters, webinars, and an online shop, targeting health-conscious German-speaking audiences. The business model focuses on content publishing and community engagement through subscriptions and educational offerings. Technically, the website is built on WordPress, hosted on AWS infrastructure, and employs modern web technologies including FriendlyCaptcha for form security. The site demonstrates good mobile optimization and SEO practices but lacks some advanced security headers and explicit cookie consent mechanisms. Security posture is solid with HTTPS and anti-bot measures but could be enhanced with formal security policies and headers. WHOIS data confirms domain legitimacy and consistency with the business. Overall, the site is professional, trustworthy, and safe for general audiences.
 compass private pflegeberatung GmbH
pflegeberatung.de
Healthcare · Germany
57Medium
NIS2 2 · GDPR 83
NIS2 2 · GDPR 83
pflegeberatung.de is a German healthcare information portal operated by compass private pflegeberatung GmbH, focusing on elder care and nursing services. The website offers comprehensive information, a search platform for care providers, and guidance for individuals and families navigating care situations. It targets a broad audience including care recipients and their relatives within Germany. Technically, the site is built on TYPO3 CMS, hosted likely by NetCologne, and integrates modern tools such as Google Tag Manager and a chatbot for enhanced user interaction. The site is well-structured, mobile-optimized, and provides a professional user experience with clear navigation and relevant content. Security-wise, the site enforces HTTPS and implements a detailed cookie consent mechanism aligned with GDPR requirements. However, it lacks explicit published security policies or incident response contacts, which could be improved. Overall, the site demonstrates a strong security posture with no detected vulnerabilities or suspicious elements, supporting its credibility and trustworthiness in the healthcare sector.
 WIENFLUSS information.design.solutions KG
wienfluss.net
Technology · Austria
75Medium
NIS2 17 · GDPR 53
NIS2 17 · GDPR 53
WIENFLUSS information.design.solutions KG is an Austrian agency specializing in accessible and user-friendly web solutions, focusing on digital accessibility and web application development. Established since 2005, the company positions itself as a leading provider in Austria for barrier-free digital services, catering primarily to organizations and institutions requiring compliant and user-centric digital products. Their key services include consulting, training, and development tailored to accessibility and usability needs. Technically, the website employs modern web standards with a modular CSS approach and JavaScript for interactivity. The site is well-structured, mobile-optimized, and includes Open Graph metadata for social media sharing. However, no advanced frameworks or CMS platforms are detected, and no analytics or tracking scripts are present, indicating a privacy-conscious approach. Performance is moderate with good accessibility features. From a security perspective, the site uses HTTPS (implied by the URL) but lacks visible security headers and explicit incident response contacts. No vulnerabilities or exposed sensitive data were detected in the HTML content. Privacy compliance is partially addressed with a privacy policy and terms of service, but no cookie consent mechanism is evident. The WHOIS data is missing or unavailable, which raises concerns about domain registration legitimacy, although the professional presentation and client list support business credibility. Overall, the website presents a professional and trustworthy digital presence with room for improvement in security headers, privacy mechanisms, and domain registration transparency. Strategic recommendations include enhancing security headers, implementing cookie consent, and verifying domain registration details to strengthen trust and compliance.
 WISTA.Service GmbH
wista-service.de
Real Estate · Germany
66Medium
NIS2 2 · GDPR 28
NIS2 2 · GDPR 28
WISTA.Service GmbH is a medium-sized German company founded in 2001, specializing in comprehensive building and facility management services at the Berlin Adlershof high-technology location. Their offerings include maintenance of buildings, laboratories, and clean rooms, as well as commercial services such as tenant management and IT infrastructure consulting. The company serves a clientele of research institutions, technology firms, and real estate developers, positioning itself as a trusted local leader with recognized certifications and memberships. Technically, the website is built on TYPO3 CMS, hosted by manitu.net, and demonstrates good performance, mobile optimization, and accessibility. Security posture is solid with HTTPS and no visible vulnerabilities, though improvements could be made by adding security headers and explicit privacy consent mechanisms. Overall, the site reflects a professional and trustworthy business presence with room for enhanced privacy and security transparency.
 WISTA.Plan GmbH
wista-plan.de
Real Estate · Germany
63Medium
NIS2 17 · GDPR 28
NIS2 17 · GDPR 28
WISTA.Plan GmbH is a Berlin-based urban development agency specializing in regional, city, and quarter planning, land development, construction, and real estate marketing. The company operates primarily in the Berlin-Johannisthal/Adlershof and Former Güterbahnhof Köpenick areas, serving businesses and stakeholders involved in urban development. The website is professionally designed using TYPO3 CMS, with good mobile optimization and accessibility features. It provides clear business information and contact details, including a physical address, phone number, and email. The presence of a LinkedIn profile adds to its credibility. Security posture is solid with HTTPS and no visible vulnerabilities, though some security best practices like security headers and cookie consent mechanisms are missing. Overall, the site is trustworthy and well-positioned within its sector.
 Sandra Elle
sandraelle.com
Media
59Medium
NIS2 17 · GDPR 35
NIS2 17 · GDPR 35
Sandra Elle is a French-language fashion and beauty blog offering personal advice, trends, and shopping tips. The website targets a general audience interested in fashion and beauty topics. Technically, the site is built on WordPress with popular plugins such as Yoast SEO and WP Rocket, ensuring good SEO and performance. The site is HTTPS secured with a Content-Security-Policy header, indicating a good security baseline. However, the absence of WHOIS data and lack of privacy and cookie policies reduce overall trust and compliance posture. No contact information or incident response details are provided, limiting transparency. Overall, the site is professionally designed and functional but would benefit from enhanced privacy compliance and clearer business information.
 Jolie Breizh
jolie-breizh.fr
Media · France
58Medium
NIS2 17 · GDPR 25
NIS2 17 · GDPR 25
Jolie Breizh is a French regional news and lifestyle website focused on the Brittany region, providing up-to-date articles across multiple categories such as news, auto, business, family, finance, real estate, leisure, home, fashion, health, and technology. The site targets a general French-speaking audience interested in regional content and lifestyle topics. Technically, the website is built on WordPress using popular plugins like Yoast SEO, WP Rocket, and Elementor, with Cloudflare DNS for domain resolution. The site is well-structured, mobile-optimized, and performs well with fast loading times. Security posture is good with HTTPS enforced and a basic Content Security Policy header, though additional security headers could improve protection. Privacy compliance is weak due to the absence of visible privacy and cookie policies or consent mechanisms. Overall, the site appears legitimate and professionally maintained, but could improve transparency and compliance aspects.
 11 Le Magazine
11lemagazine.fr
Media · France
55Medium
NIS2 17 · GDPR 10
NIS2 17 · GDPR 10
11 Le Magazine is a French online media outlet providing news and lifestyle content across various categories such as Actu, Auto, Business, Famille, Finance, Immo, Loisirs, Maison, Mode, Santé, and Tech. The website targets a general French-speaking audience interested in current events and lifestyle topics. The business model centers on content publishing with monetization likely through advertising and affiliate marketing. The site uses WordPress CMS with Elementor and WP Rocket plugins, indicating a modern and maintainable technical infrastructure. SEO is enhanced by Yoast SEO plugin and structured data implementation. Security posture is adequate with HTTPS and basic security headers, but lacks advanced headers and formal policies such as privacy and cookie consent mechanisms. No WHOIS data is available, which limits domain legitimacy verification, but the website content and technical setup suggest a legitimate media presence. Overall, the site is professional and user-friendly but could improve compliance and security transparency.
 Astuces Business
astucesbusiness.fr
Other · France
58Medium
NIS2 17 · GDPR 25
NIS2 17 · GDPR 25
Astuces Business is a French-language website focused on providing business advice, legal information, marketing strategies, and services to entrepreneurs and professionals. The site is built on WordPress and uses modern web technologies including jQuery, Google Tag Manager, and WP Rocket for performance optimization. The website demonstrates good SEO practices with structured data and meta tags, and it is mobile-optimized with a clear navigation structure. Security posture is adequate with HTTPS and a Content Security Policy header, though additional security headers could enhance protection. Privacy compliance is partial, with a cookie consent mechanism present but no visible privacy policy or terms of service pages. The absence of WHOIS data limits domain trust assessment, but the site content and technical setup appear legitimate and professional. Overall, the website serves as a niche content platform for French business audiences with moderate technical and security maturity.